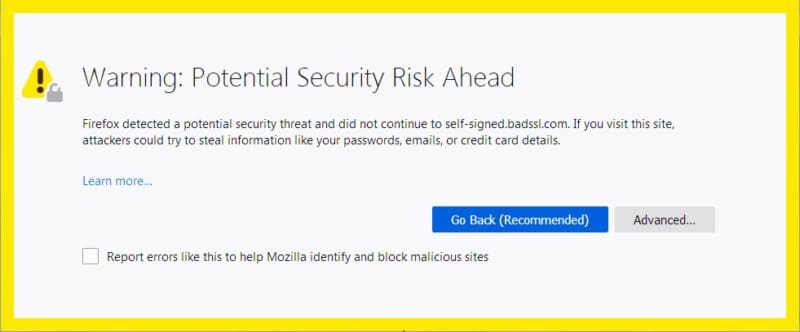



SpaceX, Microsoft, and Spotify are just some of the companies that have experienced PR nightmares because of outages caused by expired certificates – and that’s just the tip of the outage iceberg. Plenty of outages go unreported, and according to Keyfactor’s annual State of Machine Identity report, 77% of organizations experience outages due to expired certificates.
Los certificados desempeñan un papel crucial en la seguridad de los canales de comunicación y en la garantía de la privacidad de los datos. Pero a medida que el número de certificados que utilizan las organizaciones sigue creciendo, resulta cada vez más difícil gestionarlos eficazmente y saber cuándo caducan.
More than half of organizations say that outages resulted in severe disruption to customer services. But with a prevention strategy, companies can proactively avoid these disruptions before they become a problem. Here we share a practical approach to stopping certificate-related outages so you can gain full visibility and take back control of your certificates.
Por qué los certificados caducados provocan estragos
Keyfactor customer EQ Bank was plagued by sudden outages caused by unknown and untracked expired certificates. Applications would stop working, and the bank would have to pull critical resources away from day-to-day tasks to remediate outages.
Los desafíos con las interrupciones relacionadas con los certificados no se limitan a EQ Bank. En la mayoría de las empresas, el problema se atribuye generalmente a tres factores:
- More certificates, less visibility: The volume of certificates issued within a company is rising, with an average of 256,000 certificates. And while more certificates for use cases are a good thing, it also signals less visibility into the environment.
- Increasing complexity, decreasing control: Sixty-two percent of organizations don’t know exactly how many certificates they have. A company’s various teams may be using different tools and PKIs in their own way, amplifying complexity and limiting a company’s ability to oversee when certificates expire.
- Shorter lifespans, bigger risks: In September 2020, the certificate lifespan was cut in half from 27 months to 13 months. Shorter lifespans must be managed more frequently, creating more work and risk for the teams involved and the entire organization.
Un proceso de recuperación prolongado afecta al negocio
«Solo se necesita un certificado caducado para causar una interrupción, por lo que es importante tener una cobertura completa para tener la tranquilidad de que sus aplicaciones no se caerán», afirmó Sami Van Vliet, Gerente Principal de Producto para EE. UU. de Keyfactor.
Van Vliet aconseja que una buena regla general es que el número de lugares donde se utiliza un certificado caducado dentro de una empresa prolongará el tiempo que llevará recuperarse de esa interrupción. Las empresas se enfrentan a un extenso cronograma para corregir la disrupción, lo que implica identificar el certificado caducado y todas sus ubicaciones instaladas, reiniciar servicios, aprovisionar certificados, y la lista continúa.
It is a time-consuming process, and companies take more than four hours and 11 team members on average to identify, remediate, and recover from a certificate-related outage.
Pero no tiene por qué ser así.
Las empresas que toman medidas preventivas para detener las interrupciones antes de que interfieran con el negocio serán recompensadas con un tiempo de inactividad menos costoso y una disrupción minimizada.
Recupere el control de los certificados con automatización
Con visibilidad de extremo a extremo, gestión de certificados y automatización del ciclo de vida, las empresas pueden prevenir interrupciones relacionadas con los certificados. Keyfactor sugiere lograr esta trifecta de prevención adoptando un enfoque de «gatear, caminar, correr». Comience por obtener visibilidad de los certificados en sus CA, redes y dispositivos. Identifique dónde residen, quién los emitió y cuándo caducan.
Once you understand what is out there, you can move forward with actively managing and monitoring your certificate inventory. Do this by enforcing policies and setting renewal alerts to ensure end-users renew certificates before they expire.
La última fase consiste en automatizar completamente los procesos de renovación y aprovisionamiento de cada certificado en cada máquina. La automatización reduce la fricción y el riesgo, lo que le permite identificar y remediar rápidamente los certificados caducados para adelantarse a las interrupciones inesperadas.
The crawl, walk, run approach helped EQ Bank solve its problem with outages caused by expired certificates. Using a combination of expiration alerting and automated renewal workflows, Keyfactor Command centralized visibility and significantly reduced the rate of human error. EQ Bank has not experienced a single certificate-related outage since running with Keyfactor Command.
To learn more about Keyfactor’s approach to preventing certificate-related outages, watch the on-demand webinar Crawl, Walk, Run – A Practical Approach to Preventing Certificate Outages.
Suscríbase a The Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.