


There is a lot to learn from last week’s news regarding Google’s decision to distrust Entrust for Google Chrome. Any certificate issued from Entrust root certificate authorities (CA) after October 31, 2024 will no longer be trusted by the Google Chrome browser.
According to reports, Google’s decision to part ways with Entrust’s public certificate authorities (CAs) is due to an “observed pattern of compliance failures, unmet improvement commitments, and the absence of tangible, measurable progress in response to publicly disclosed incident reports.” Digital certificates have been mis-issued which has led to overall security implications. While unfortunate, Google’s response is intended to preserve the integrity of Web public key infrastructure (PKI). In today’s increasingly digital world, PKI is critical to protect the confidentiality and authenticity of communication between web browsers and web content servers. PKI is what ensures digital trust in our online world.
¿Qué significa esto para las empresas?
Las empresas que deseen que sus sitios web y aplicaciones de cara al público sean accesibles mediante el navegador Chrome, que representa más del 65% de todos los usuarios de Internet, tendrán que planificar la migración y asegurarse de que los certificados emitidos por Entrust que estén a punto de caducar se renueven y sustituyan por certificados emitidos por otra CA de confianza pública.
¿Qué podemos aprender de esta decisión?
There are four major lessons from Google’s recent decision to distrust Entrust.
First is the importance of CA-agility. When it comes to leveraging public CAs, there is always the risk that a CA will revoke certificates or be distrusted from web browser trust stores (this has happened several times in the past few years). To minimize this risk and prevent disruption, businesses must maintain the ability to easily add, switch, and migrate CAs, or have a multi-CA strategy.
Second is the critical need for crypto-agility. Every CA makes mistakes and web browsers are forced to make the difficult decision to revoke certificates. In fact, this has happened several times over the last year, such as Mozilla’s distrust in Entrust public CAs in May. Organizations must be able to handle revocations at scale and install new certificates in place of old ones, without disrupting business operations.
Third, businesses shouldn’t put all their eggs in one public CA’s basket. Companies should also avoid using public CAs for anything other than entities that require public trust, such as public-facing websites and applications (i.e., for a mobile app that speaks to the cloud). With private PKI, encryption within an organization’s internal servers and systems is deployed to verify the authenticity of users and devices. In this instance, private CAs are created to issue certificates and they are managed internally, reducing the risk of unauthorized access and potential compromise by external entities.
En nuestro mundo digital, la confianza lo es todo y la PKI privada permite a las empresas ofrecer a quienes confían en sus CA un mayor grado de confianza.
Fourth, this situation is an early warning sign of what’s to come for post-quantum cryptography (PQC). Replacing all publicly trusted certificates from a CA is a drop in the bucket compared to what will be required to migrate to quantum-safe algorithms. This decision is a good reminder that businesses must start planning for the transition to PQC algorithms as early as possible to avoid catastrophic disruptions.
How can Keyfactor help?
Como preparación para el próximo cambio en Chrome, los responsables de TI y seguridad deben evaluar detenidamente su PKI y su entorno de certificados. Las empresas deben actuar con rapidez para identificar y sustituir los certificados afectados, y este es un proceso que no puede hacerse manualmente.
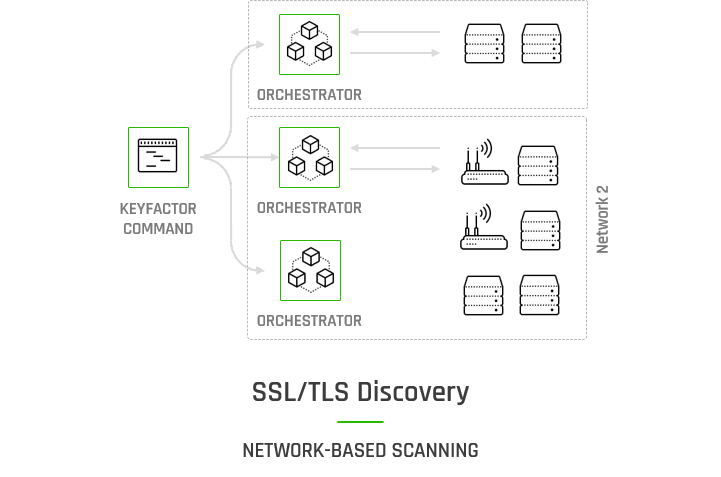
With Keyfactor Command, customers gain the visibility and automation needed to make the transition to a new CA seamlessly. Keyfactor Command gives businesses a view into all their certificates from a single dashboard, helping them to identify and remediate risks fast with a simple search-and-click engine.
Los usuarios también pueden aprovechar Keyfactor Orchestrators y los plugins preconstruidos para automatizar la renovación, el aprovisionamiento y la instalación de certificados con un solo clic o sin ningún clic. Para aquellos que utilizan los certificados digitales de Entrust, las ofertas de Keyfactor's Command proporcionan la flexibilidad necesaria para migrar la PKI y la gestión de certificados sin interrupción de la productividad.
When it comes to preparing for PQC, businesses can leverage Keyfactor’s PQC Lab – a free, SaaS-based sandbox that enables teams to generate a PQC-ready CA and start issuing quantum-resilient certificates in minutes. The sandbox is now available in Azure.
Claves para la gestión de certificados en el futuro
La decisión de Google de desconfiar de Entrust es una llamada de atención para las organizaciones. La confianza digital no es estática; siempre está amenazada.
Para seguir siendo resistentes, las empresas necesitan una visibilidad total de todos los certificados, la capacidad de automatizar la sustitución y corrección de certificados a escala y, lo que es más importante, la flexibilidad para añadir, migrar o cambiar de CA, sin causar interrupciones.
To learn more about how Keyfactor can help your organization navigate this transition, please reach out here.
Suscríbase a The Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.