


El mundo digital funciona con sistemas interconectados y software. El cifrado es lo que lo hace posible.
Public key infrastructure, or PKI, serves as the foundation for digital trust, enabling authentication, encryption, and integrity, all essential to securing connections across your business. Today’s digital collaboration and innovation couldn’t exist without the simple principle of secure handshakes between users and devices on the internet.
The number of certificates is growing exponentially in the face of global networks, more connected devices, and an increased remote workforce. Failed authentication can throw a wrench in your operations. Implementing a nimble, automated solution can set your IT or security department up for success in the face of changing technologies and threats, reduce human error, and save valuable time.
Este artículo detalla los aspectos clave que debe conocer sobre la tecnología PKI y cómo permite a su organización ampliar las operaciones empresariales de forma segura.
¿Qué es la PKI?
PKI es una infraestructura criptográfica que utiliza claves públicas y privadas para la seguridad digital. La PKI permite las comunicaciones cifradas, la autenticación sin contraseña y la integridad de los datos. Los certificados se utilizan como prueba de verificación entre las dos claves, indicando que la relación entre dispositivos o usuarios es segura y no ha cambiado. Gran parte del mundo digital utiliza la autenticación PKI para verificar sistemas, usuarios y aplicaciones. Los certificados SSL de los sitios web, por ejemplo, verifican la legitimidad de los mismos.
Para gestionar el intercambio constante de información, las autoridades de certificación (CA) almacenan, emiten y firman certificados digitales, y las autoridades de registro (RA) verifican la identidad de las entidades que solicitan sus certificados digitales a la CA. Los niveles sucesivos de certificados crean una jerarquía, construyendo una red de confianza entre dispositivos, aplicaciones y usuarios.
For additional security, PKI certificates have expiration dates, the lengths of which vary depending on the certificate. Certificate lifespans can range anywhere from one year to one day, even just minutes, with ephemeral workloads. An expired certificate is no longer trusted, making PKI certificate maintenance essential to prevent unexpected system outages. And because this network of trust includes unique keys, an organization may need millions of certificates to authenticate a fully remote, multi-device workforce.
With the average organization surveyed in our 2024 PKI and Digital Trust Report report managing over 81,000 certificates, keeping track of tens of thousands of authentication certificates from multiple CAs manually is nearly impossible.
Los nuevos avances tecnológicos afectan a los cambios en las mejores prácticas para los certificados. Con el tiempo, los periodos de caducidad se han acortado y la longitud de las claves ha aumentado; a medida que evolucione la computación cuántica, serán necesarios nuevos algoritmos para mantener la seguridad a nivel empresarial y la confianza digital que experimentamos hoy en día.
¿Cómo funciona la autenticación basada en PKI?
La base de la PKI es el cifrado mediante algoritmos criptográficos, que convierten un simple mensaje en una serie de caracteres aleatorios que sólo pueden descifrarse con una clave. El cifrado simétrico utiliza la misma clave para cifrar y descifrar un mensaje. Esto plantea un problema para las comunicaciones seguras: ¿cómo comunicarse con otra parte sin compartir la misma clave?
To prevent that risk of compromise, researchers developed asymmetric cryptography to securely exchange information between two parties. Public keys allow each party to send encrypted messages that can only be decrypted using the recipient’s private key. The same process can be used to authenticate the legitimacy of entities.
Consider this example
Si Alice quiere demostrar su identidad a Bob, puede enviarle un mensaje cifrado que diga : "¡Eh, Bob! Soy yo, Alice".
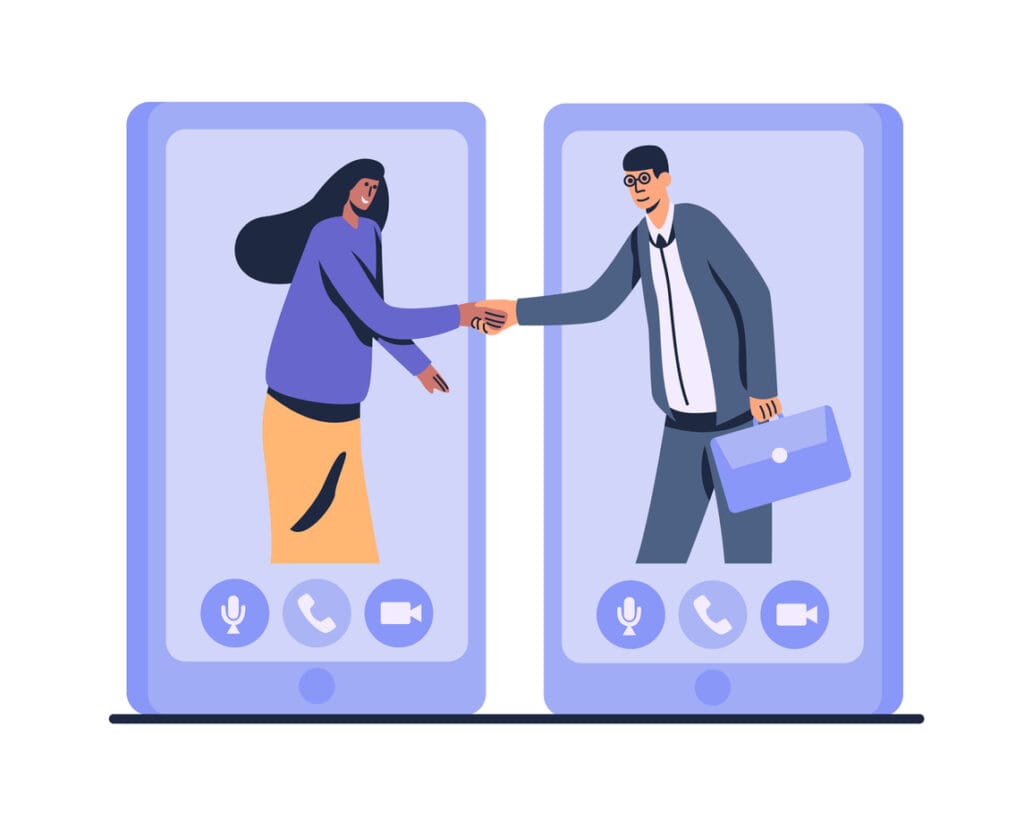
First, Alice needs her own key pair, which she can obtain in a certificate via a certificate authority. The CA may require Alice to provide some ID first, such as a driver’s license. Bob also needs a certificate, because Alice can’t craft a special message just for Bob without Bob’s public key. After a quick handshake, Alice can send her message to Bob, who then verifies the authenticity of the sender (Alice) because her certificate was issued by a trusted authority.
Casos de uso habituales de PKI
Hoy en día, la autenticación PKI se utiliza para proteger su actividad en Internet:
- Secures websites: The familiar lock symbol on websites indicates an SSL/TLS certificate verifying the site’s identity and encrypting communication, protecting your data from eavesdroppers.
- Ensures software and code authenticity: Digital signatures act like tamper-proof seals on code, giving you peace of mind that you’re installing or using the real deal.
- Protects IoT devices: In the ever-expanding world of smart home devices, PKI secures communication between them and cloud services, safeguarding your data, enabling new capabilities like firmware updates, and preventing unauthorized access.
- Granular access control: PKI acts as a gatekeeper for sensitive company resources on intranets and VPNs, restricting access only to authorized users like in a zero trust model.
- Password-free Wi-Fi convenience: Forget complex Wi-Fi passwords! PKI can enable secure access based on device ownership, streamlining the process.
- Encrypts email and data: S/MIME, powered by PKI, encrypts your emails and data, ensuring only intended recipients can access the information.
These are just a few examples of how PKI forms the backbone of trust and security in today’s digital world. PKI certificates protect users, devices, and systems from unauthorized breaches, continuously assuring the veracity of the data exchanged.
Conclusiones sobre PKI
La infraestructura de clave pública es la base de la confianza digital. A medida que aumenta nuestra dependencia de los sistemas interconectados, también lo hace la complejidad de la gestión de la ICP. La gestión manual de millones de certificados es propensa a errores y obstaculiza la innovación.
En comparación, adoptar una solución automatizada ayuda a su organización a agilizar la gestión de certificados, liberando a los equipos de TI y seguridad para que puedan centrarse en iniciativas estratégicas. Este cambio permite a su empresa:
- Build a strong foundation: A robust PKI system lays the groundwork for secure communication and fosters trust with customers and partners.
- Enhance agility: Automated PKI management allows for quicker scaling and adaptation to evolving security threats and technological advancements.
- Improve security posture: Automating mundane tasks minimizes human error and ensures certificates remain valid, preventing security vulnerabilities or outages.
PKI es una tecnología fundamental que puede optimizarse para satisfacer las demandas del futuro. Al adoptar la automatización y centrarse en soluciones fáciles de usar, las organizaciones pueden utilizar la PKI para construir un ecosistema digital seguro y adaptable. El futuro de la PKI es brillante, con la confianza y la seguridad entretejidas a la perfección en el tejido de nuestro mundo interconectado.
Comienza tu viaje
Is your growing business ready to centralize the management of PKI authentication? Keyfactor can help you implement a powerful, nimble solution. Watch a demo to see the power of automated PKI certificate management.
Suscríbase a The Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.
Continuar leyendo
Una Retrospectiva de un Fantástico 2021 – y el Camino Hacia un Futuro Apasionante
Leer más
Cómo mantenerse a la vanguardia de la escasez de talento en ciberseguridad
Leer más