


La confiance numérique est essentielle à la sécurité de tous les objets connectés, qu'il s'agisse de stimulateurs cardiaques, d'imprimantes, de moyens de transport ou d'infrastructures critiques. Et comme l'utilisation de ces dispositifs IoT continue d'exploser, il n'a jamais été aussi important de comprendre les tendances en matière de confiance numérique.
With that in mind, Keyfactor and Vanson Bourne partnered on a report, Digital Trust in a Connected World: Navigating the State of IoT Security, which draws insights from 1,200 survey responses from two unique perspectives – those who design and manufacture connected devices/products (OEMs) and those who deploy and operate connected devices/products within their organization.
Ready to dig into the data? Ellen Boehm, SVP of IoT Strategy and Operations at Keyfactor, and Mitch Mershon, Product Manager for Emerging Markets at Keyfactor, sat down to discuss key findings from the report, including trends in IoT device identity and management, the prevalence and impact of security breaches, and the impact of industry standards on product development. Read on for a recap of their conversation, or click here to watch the webinar.
Établir la confiance numérique : Tendances en matière de gestion des dispositifs et des identités sur le site IoT
First and foremost, it’s essential to start with the building blocks of digital trust: Every machine needs an identity, and every identity must be managed.
Traditionally, we think about identity management from the enterprise perspective, meaning server racks, laptops, and other devices on a corporate network. But we now live in a world of smart, connected devices that extend everywhere and to everyone, and each of those IoT devices needs an identity because each one represents an attack vector.
These modern devices can also be very complex, in some cases even a machine of machines. Think about a car or a plane – each has many different components with its own operational networks that can connect to the corporate network. In these cases, we have a machine with multiple identities inside it with its own broader identity that connects into a system.
So, how exactly does all of this work? First, you have manufacturers, designers, and developers that make an IoT device, whether a wind turbine, a train, a drone, or anything else. These OEMs handle efforts like security design, testing, certification, and identity provisioning. Once the device is produced and sold, it’s deployed into a facility such as a factory, hospital, or utility grid, where operators take over and manage service deployment, device health monitoring, and end-of-life decommissioning. Fortunately, both teams’ budgets for IoT device security will continue to increase year over year. According to our report, leaders expect a 45% increase in the next five years, which shows that IoT security is a priority investment for companies because they understand the risks it can have on the business if done incorrectly. However, 52% of that budget could be at risk if it needs to be diverted to handle cleanup after the fact, such as in the case of an outage or a compromise. This is notable because cyber attacks are on the rise.
Comprendre les risques : La prévalence et l'impact des failles de sécurité sur les appareils IoT
Les failles de sécurité se multiplient et personne n'y échappe : Presque toutes les entreprises ont déjà été victimes d'une cyberattaque et celles qui ne l'ont pas encore été le seront probablement dans un avenir proche. En fait, 89 % des répondants à l'enquête ont déclaré que les produits IoT de leur organisation avaient fait l'objet d'une cyberattaque au cours des 12 derniers mois, et 69 % ont déclaré avoir constaté une augmentation des attaques sur les appareils IoT au cours des trois dernières années.
La raison de cette augmentation est que IoT est utilisé partout : Les répondants à l'enquête font état d'une augmentation de 20 % de l'utilisation des appareils IoT au cours des trois dernières années. Plus d'appareils signifie plus d'identités (à la fois des identités plus larges pour chaque appareil et toutes les identités des petites machines qu'il contient), ce qui multiplie le nombre de vecteurs d'attaque.
For example, manufacturing used to be a tight, close-knit system, but now all the new machinery is connected with different sensors within each unit. Each of those sensors, plus the machinery at large, is an attack vector. Or consider the case of supply chain management, where one company talks to another and another and another, creating a chain. In both cases, operators must ensure they can trust every single identity and communication along the way to secure against attacks, even from seemingly innocent devices like an HVAC unit.
Et le coût de ces attaques n'est pas négligeable :
- $236,000 is the average cost that companies have paid as a result of a breach in the past year because their IoT devices were able to leak data or someone was able to get in through a device into the network. Considering that number is from one year, it’s easy to imagine how that starts to add up over time.
- $2.3 million is the average cost for a certificate outage on a manufacturing line, meaning if a connected device tries to call a server, but the certificate is invalid, the factory line can no longer produce until the issue is fixed.
Il ne s'agit pas seulement d'argent. Selon les personnes interrogées, les principales préoccupations à la suite d'une cyberattaque sont les suivantes : atteinte à la réputation externe, perte de données sur les clients, perte de confiance des employés dans l'organisation, amendes réglementaires et perte de revenus.
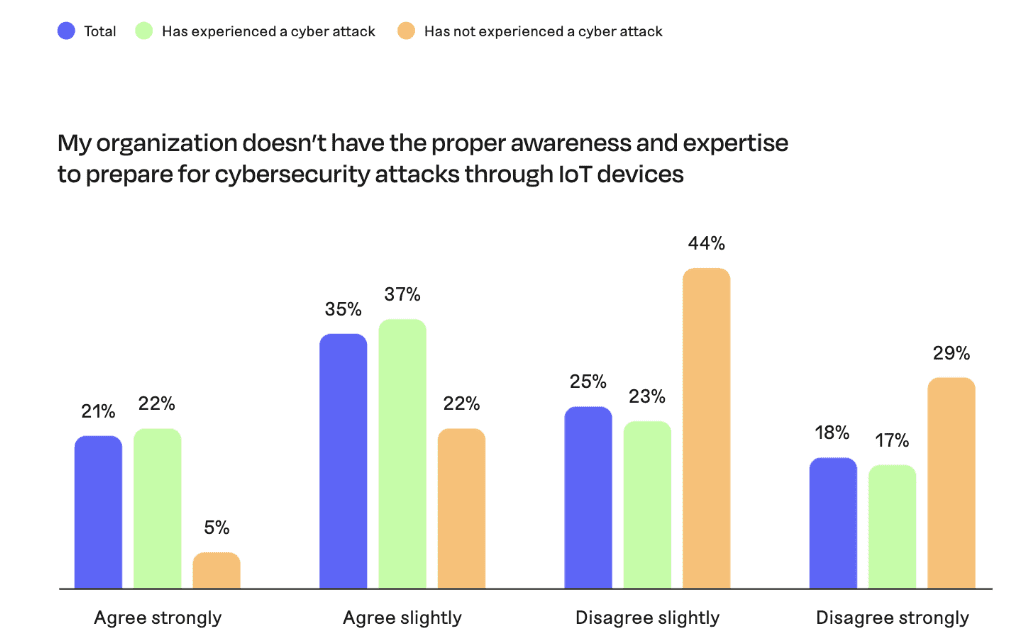
Dans l'ensemble, les personnes interrogées reconnaissent que la sécurité de leur site IoT doit être améliorée (88 %) pour se protéger contre ces risques. Cela dit, 47 % des personnes interrogées estiment qu'elles font déjà tout ce qu'elles peuvent pour protéger leur organisation. En y regardant de plus près, 56 % des personnes interrogées reconnaissent que leur organisation ne dispose pas de la sensibilisation et de l'expertise nécessaires pour se préparer à des attaques de cybersécurité par le biais des dispositifs IoT . Ce chiffre passe à 59 % si l'on considère les données de l'enquête. Ce chiffre passe à 59 % si l'on considère uniquement les organisations qui ont déjà subi une cyberattaque, contre 27 % pour les organisations qui n'ont pas encore subi d'attaque.
Fortunately, even though attacks are rising and security is challenging, protection is possible. It requires having complete visibility into IoT devices and their identities, including the ability to quickly find those identities as needed and automate lifecycle management activities so that devices don’t go down and everything stays operational, even as certificates expire or become compromised. It also requires partnering with a company that has the proper expertise in IoT security to fill in potential gaps on the internal team.
Intégrer la sécurité dès le départ : Les principales tendances pour que les équipementiers prennent la responsabilité de la sécurité sur le site IoT
Si l'on se concentre sur les équipementiers, trois tendances se dégagent en ce qui concerne la sécurité sur le site IoT :
1. Security must be at the heart of product design: OEMs understand that having proper security architecture from the beginning of product design is just as important as the electronics, functionality, and the software itself. That’s because if security isn’t done correctly, it becomes impossible to do things like send secure firmware updates remotely, activate new features, or upsell customers. As a result, more manufacturers are considering security from the beginning.
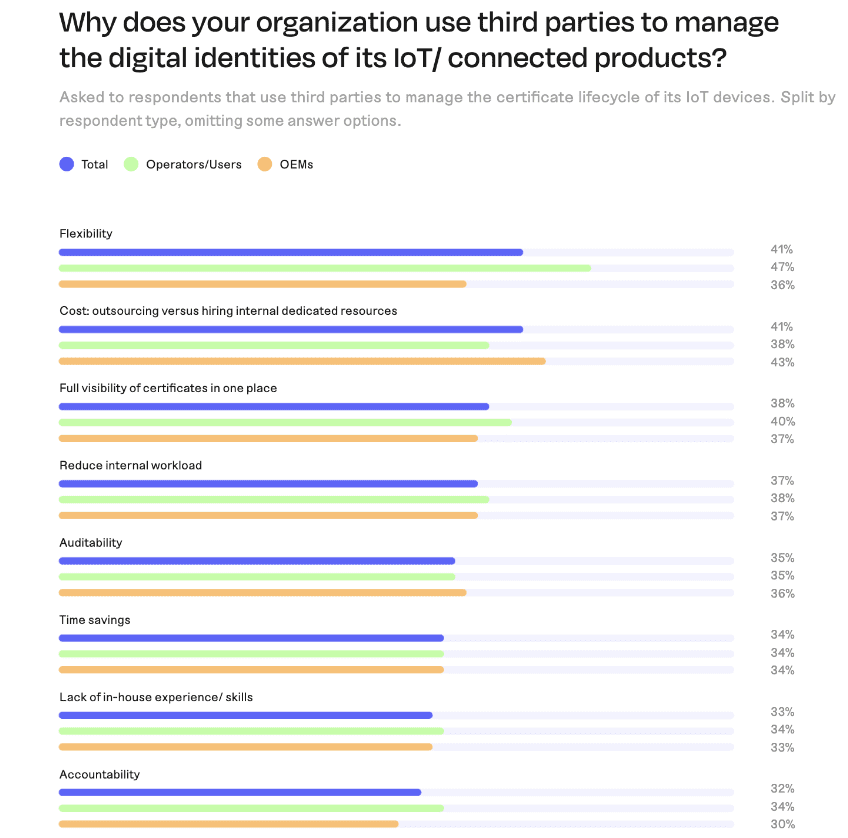
2. Third-party partners provide the expertise to implement security effectively: We’re also seeing more collaboration within the ecosystem as manufacturers realize they don’t need to develop everything from scratch. Now, OEMs are looking to implement best practices from across the field and work with expert partners to implement the best security possible. This approach is also essential as manufacturers think about how technology will change and how they can make their designs flexible enough to be used in the field for 10-15 years. According to respondents, the top reasons to partner with third parties include greater flexibility and cost from a resourcing perspective, the ability to gain complete visibility into hundreds of millions of device identities, and reducing internal workloads around a highly niche skill.
3. Security doesn’t end when the device rolls off the line: Security is not just about what the device looks like when it’s first produced. Rather, OEMs are responsible for security for the entire lifetime of the device. Think about a software update on an iPhone: When a user clicks “install,” the phone first validates that the firmware has a certificate. It does a signature verification before installing anything to know where the update is coming from and that it can be trusted. This ongoing verification is essential to security.
Tout cela est d'autant plus important que même si chacun peut se préparer à une expérience sécurisée, des brèches se produisent. Et lorsqu'une faille survient sur un appareil IoT , plus de 70 % des personnes interrogées estiment que le fabricant est au moins en partie responsable.
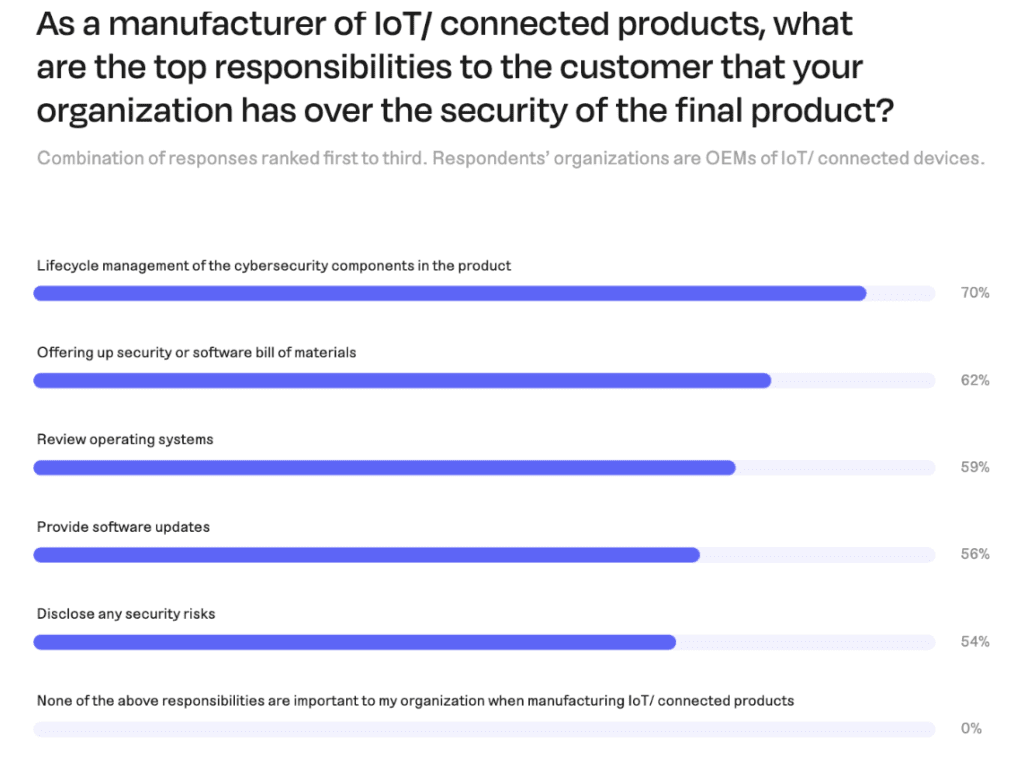
Dans cette optique, les équipementiers considèrent que leur principale responsabilité (parmi d'autres) est la gestion du cycle de vie des composants de cybersécurité à l'intérieur des produits. Parmi les autres responsabilités importantes, citons le partage d'une nomenclature de sécurité ou de software , l'examen des systèmes d'exploitation et la fourniture de mises à jour de software .
Adopter les normes de l'industrie : L'impact des réglementations sur le développement des produits IoT
Even with all the progress manufacturers and operators are making regarding IoT security, there’s still a lack of clarity around best practices. And that’s mainly due to the fact that regulations vary significantly from one country to another. Keeping up with these standards is another reason why partnering with third-party experts benefits OEMs.
Looking at the big picture, standards are becoming more common and having a much more significant impact on product development. For example, Matter’s open-source connectivity standard for smart home and IoT devices is one of the most recognized standards to come together over the past several years. The automotive industry has also led the way with various regionally-based standards.
Regardless of the industry, many manufacturers must make changes to meet these standards. If they don’t, they either can’t sell their product due to governmental regulations, or they’re missing out on part of the market thanks to consortiums like Matter. The fact that these regulations can now impact sales and market fit – not to mention that end users are starting to expect products to meet specific standards – has forced manufacturers to adjust how they do business, and that trend will only continue.
IoT La sécurité évolue : Les équipementiers et les fournisseurs doivent suivre le rythme
L'état de la sécurité du site IoT a énormément évolué au cours des dernières années, et nous atteignons aujourd'hui un nouveau niveau de risque.
As IoT devices become so much more prevalent across the entire world, they’re increasingly becoming attack vectors. At the same time, both manufacturers and users admit that they lack the proper expertise to secure these devices. Already, this situation has led to severe ramifications from breaches that extend well beyond immediate financial impacts, such as reputational damage and audit risks.
En réponse, les équipementiers et les fournisseurs doivent donner la priorité à la sécurité sur le site IoT en l'intégrant dès le début et en s'associant à des experts qui peuvent aider à combler les lacunes en matière de connaissances, à maintenir une sensibilisation adéquate et à adhérer à des normes nouvelles et changeantes. Lorsque cela se produira, les organisations seront sur la bonne voie pour se protéger contre ces risques croissants.
S'abonner à La Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.
Lire la suite

Maisons intelligentes, sécurité plus intelligente : comment les fabricants d'appareils domestiques intelligents assurent une connectivité sécurisée
En savoir plus
Pas de statu quo : ce que les fabricants d'IoT doivent savoir sur la loi sur la cyber-résilience
En savoir plus