¿Dispone de métricas de PKI? Estas son las principales que debe conocer.




Si ha pasado algún tiempo en el espacio de la ICP, es probable que haya oído hablar mucho de la criptoagilidad últimamente, pero ¿qué significa realmente?
La criptoagilidad consiste en preparar para el futuro los elementos de su programa PKI, como los algoritmos de firma y los puntos fuertes de las claves, para tener en cuenta las próximas evoluciones. Por ejemplo, ahora se habla mucho de prepararse para la computación cuántica, lo que implica actualizar y reforzar las claves para que se mantengan al día con la evolución de los estándares.
En última instancia, lograr la agilidad criptográfica se reduce a cuatro áreas críticas:
- Visibilidad de todas sus claves y certificados
- Controlar esos elementos para asegurarse de que cumplen las políticas adecuadas.
- Automatización de la renovación de certificados para evitar interrupciones frente a la pérdida de renovaciones manuales
- Orquestar esas pólizas y renovaciones en todas sus diferentes cadenas de herramientas o canalizaciones DevOps mediante la integración con soluciones como Istio y HashiCorp.
Todas estas áreas son importantes, pero la visibilidad es la más importante para empezar. Esto se debe a que si no conoce el estado de su criptografía, las operaciones de PKI se vuelven extremadamente difíciles. Y cuando se trata de visibilidad, estas son las diez métricas más importantes que hay que controlar.
1) Estado de expiración
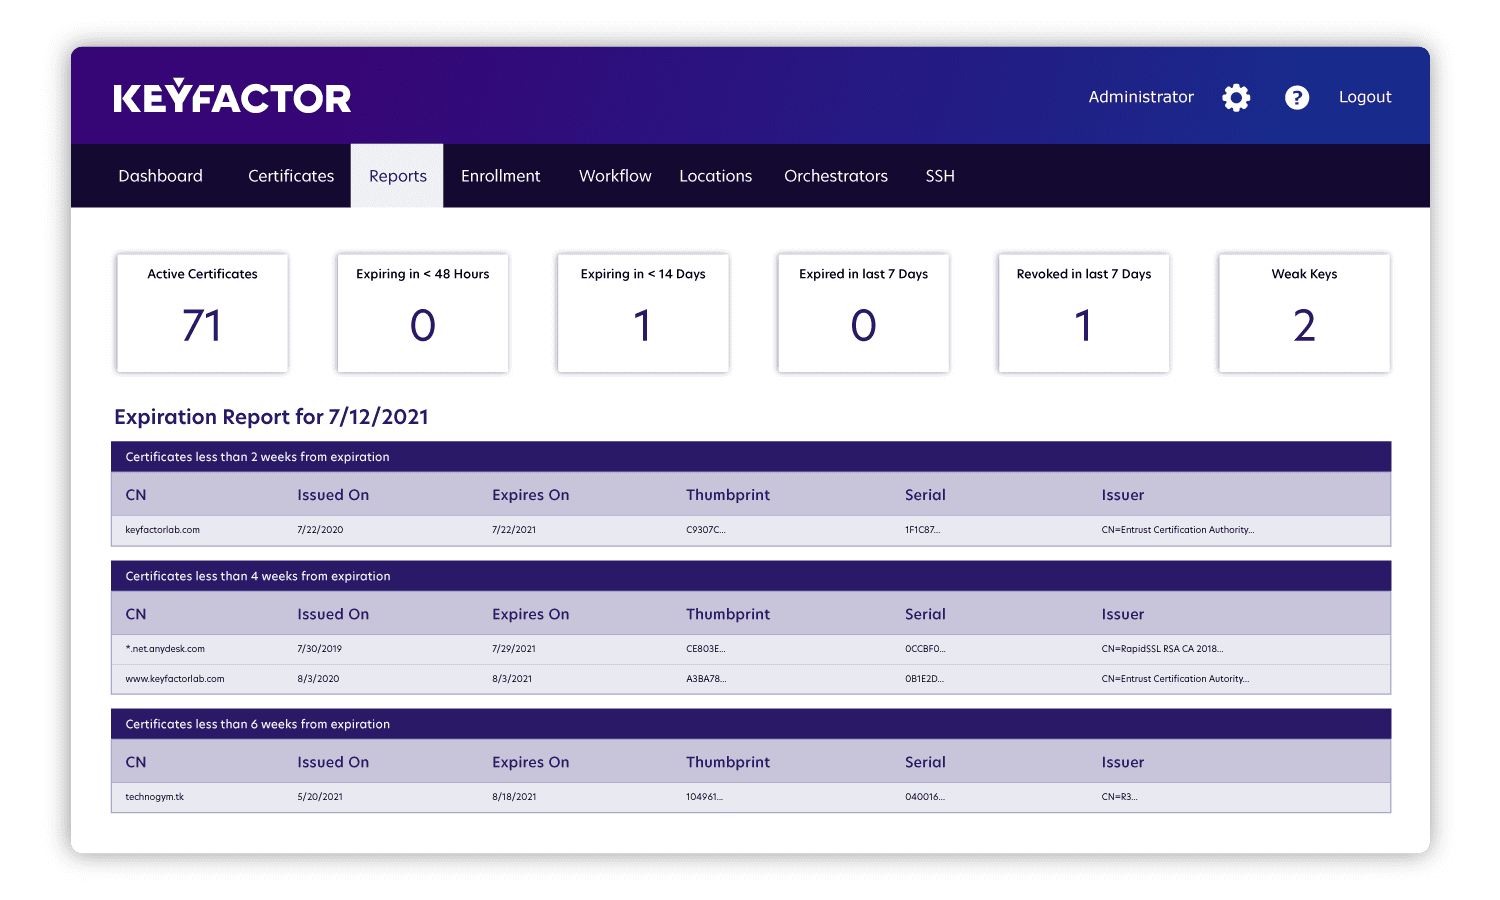
What to track: Gaining visibility into every certificate’s expiration status, including when they’re going to expire and who needs to be notified before that happens, can make an enormous difference for your PKI program. Otherwise, you run the risk of network outages, and that risk only multiples alongside the growing number of identities in the enterprise.
Why to track it: Expiring certificates are the leading reason organizations start doing certificate lifecycle management, particularly when an outage reinforces the importance of these activities.
Importantly, expired certificates can lead to more than just outages. In this example, the company had an expired certificate on a server that was monitoring network traffic. Because the certificate expired, it wasn’t reporting the data exfiltration that released customers’ personally identifiable information onto the internet. Once the company replaced the certificate (which took about 19 months past its expiration), they started seeing that theft. This is an example where the certificate didn’t cause an outage and, due to a lack of visibility into expiration status, the company didn’t immediately notice anything wrong.
How to track it: The best way to get visibility into expiration status is through a report that gives an overview of all your certificates and when they are going to expire, that way you can prioritize which ones you need to take action on. This visibility also gives you a chance to plan for the renewals that will take more time (e.g. in cases where you don’t know who’s in charge of a certificate or you don’t know how to replace it on the application that’s using it).
2) Tamaño y fuerza de la llave
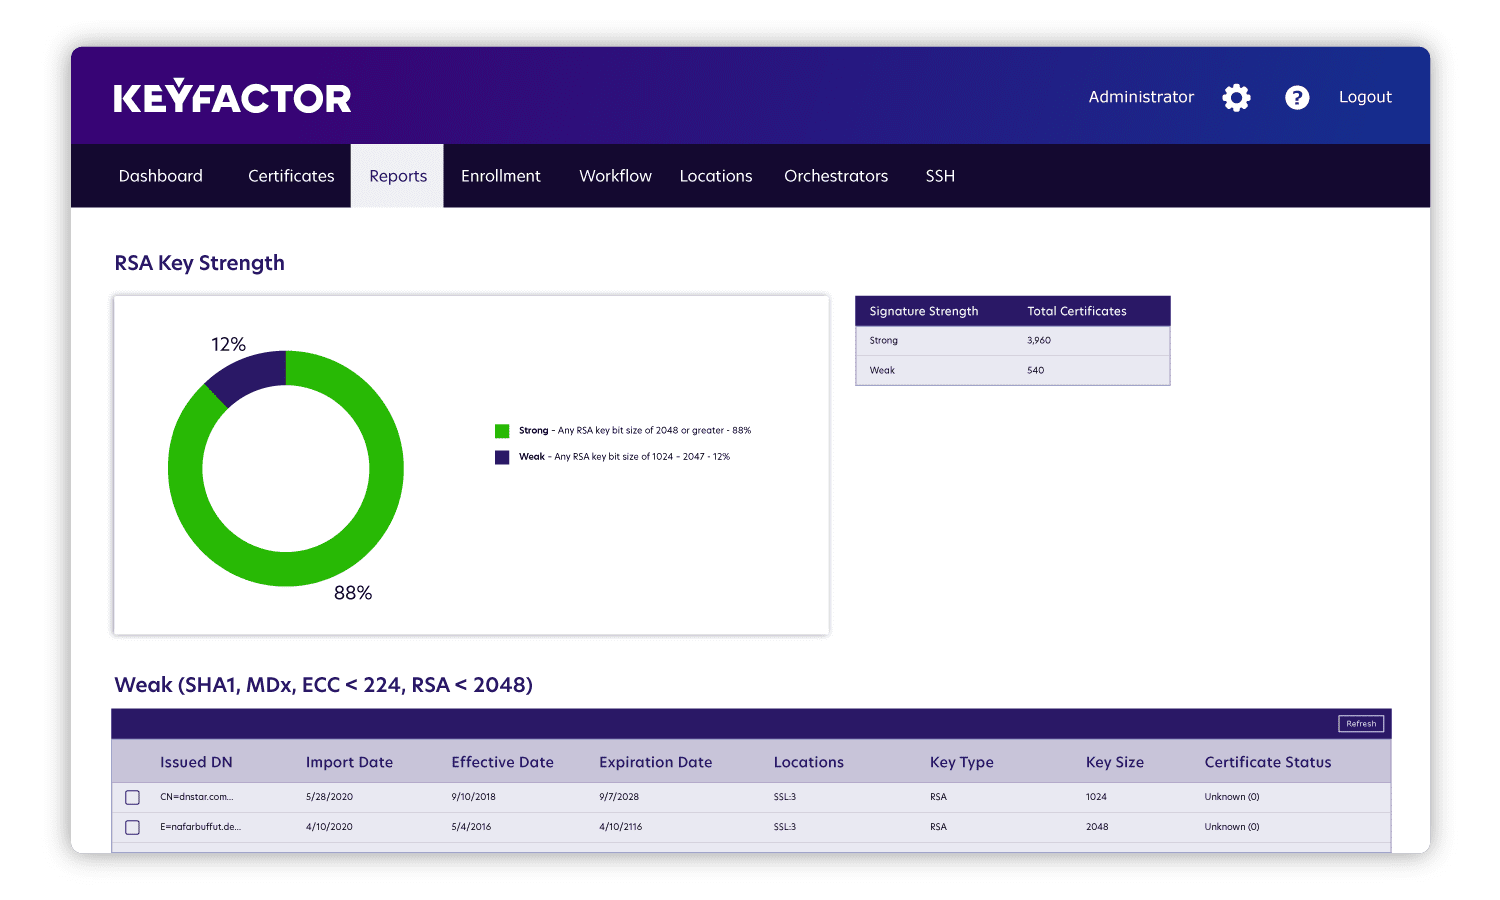
What to track: Understanding the size and strength of all your keys and certificates is also essential. Having this visibility can help you determine if your keys are weak and avoid becoming vulnerable to an attack as a result.
Why to track it: Every time we experience advances in computing, the algorithms behind cryptographic keys need to evolve. And given how often this happens, it’s important to make sure you can adapt key size and strength quickly, with minimal disruption to your existing infrastructure.
Además, una clave muy débil podría indicar que tienes algo tan antiguo que ya ni siquiera se utiliza, ya que muchas aplicaciones simplemente rechazan certificados basados en estándares tan bajos. Como resultado, rastrear el tamaño y la fuerza de la clave también puede ayudar a identificar casos de sprawl.
How to track it: The ideal report for this metric evaluates key size and strength to provide an overview of where you may have vulnerabilities. For example, is the issue that your key strength is too low or is it that you have a weak signing algorithm? The answers to these questions should offer insight into where you need to adjust your settings to maximize the strength of your keys so that you don’t have to update them again in a short time frame.
3) Algoritmos de firma
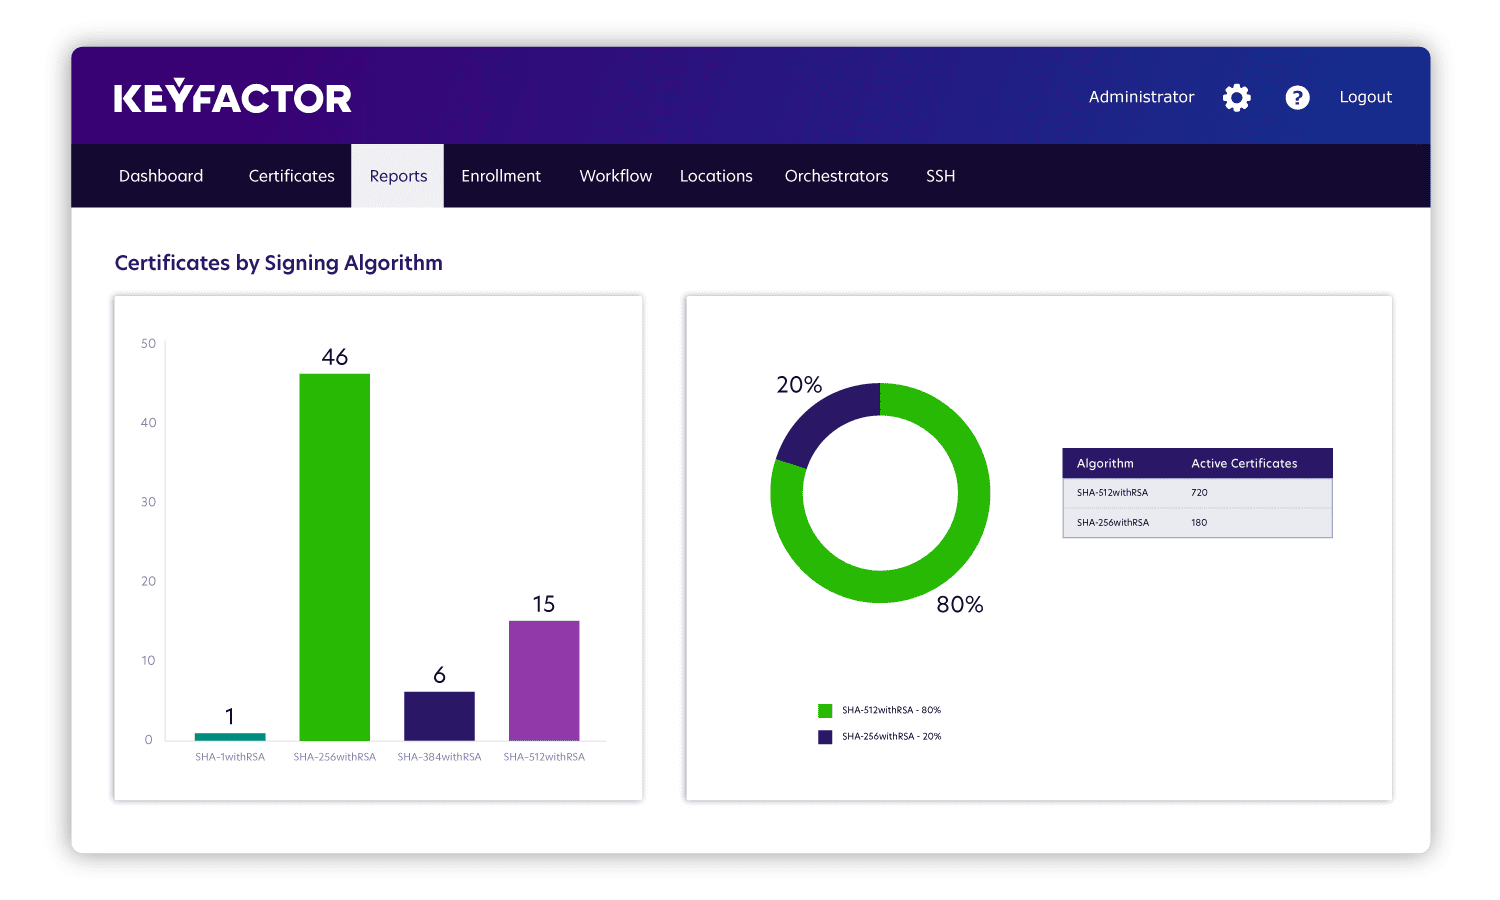
What to track: Signing algorithms are the foundation of trust and security for PKI. Similar to key size and key strength, it’s essential to track signing algorithms and prepare for migration if the algorithm will be deprecated.
Un ejemplo bien conocido de esto es la migración de SHA-1 a SHA-2. Cuando esto ocurrió, aunque el algoritmo de firma SHA-1 estaba obsoleto, muchas aplicaciones no se habían puesto al día para poder utilizar los nuevos certificados SHA-2, por lo que esos proyectos de migración requerían un enfoque muy consciente basado en qué aplicaciones estaban consumiendo esos certificados.
Why to track it: Even though larger hashes are generally more secure as they’re less vulnerable to collision attacks, the definition of larger constantly changes. For instance, right now we’re waiting for advice from NIST around quantum cryptography and quantum computing. Something could happen tomorrow that requires us to apply changes quickly, and we need to be prepared for that.
En el momento en que alguien consiga un ordenador cuántico capaz de romper los algoritmos SHA-2, todo el mundo tendrá que volver a emitir certificados con un algoritmo mucho más potente. Por eso es fundamental poder hacer un seguimiento de lo que se ha actualizado y disponer de automatización para sustituir esos algoritmos rápidamente a escala (en Keyfactor, hemos reemitido y desplegado millones de certificados en 24 horas).
Curiosamente, a veces encontramos dispositivos IoT diseñados sin tener en cuenta la agilidad criptográfica porque los certificados tienen una vida útil de 20 años y cualquier actualización requiere ir manualmente a cada dispositivo y sustituir el certificado. Esto no sólo supone un coste enorme, sino que los cambios en los algoritmos a lo largo del tiempo dejarán esos dispositivos extremadamente vulnerables.
How to track it: The most helpful reports look at how many applications have been migrated, how many haven’t been migrated and what’s needed to get those remaining ones migrated. In cases like the SHA-1 to SHA-2 migration, which centered around applications’ inability to consume the updated signing algorithm, this report is also valuable in helping application owners understand what security updates they need to make.
4) Emisión de autoridades de certificación (AC)
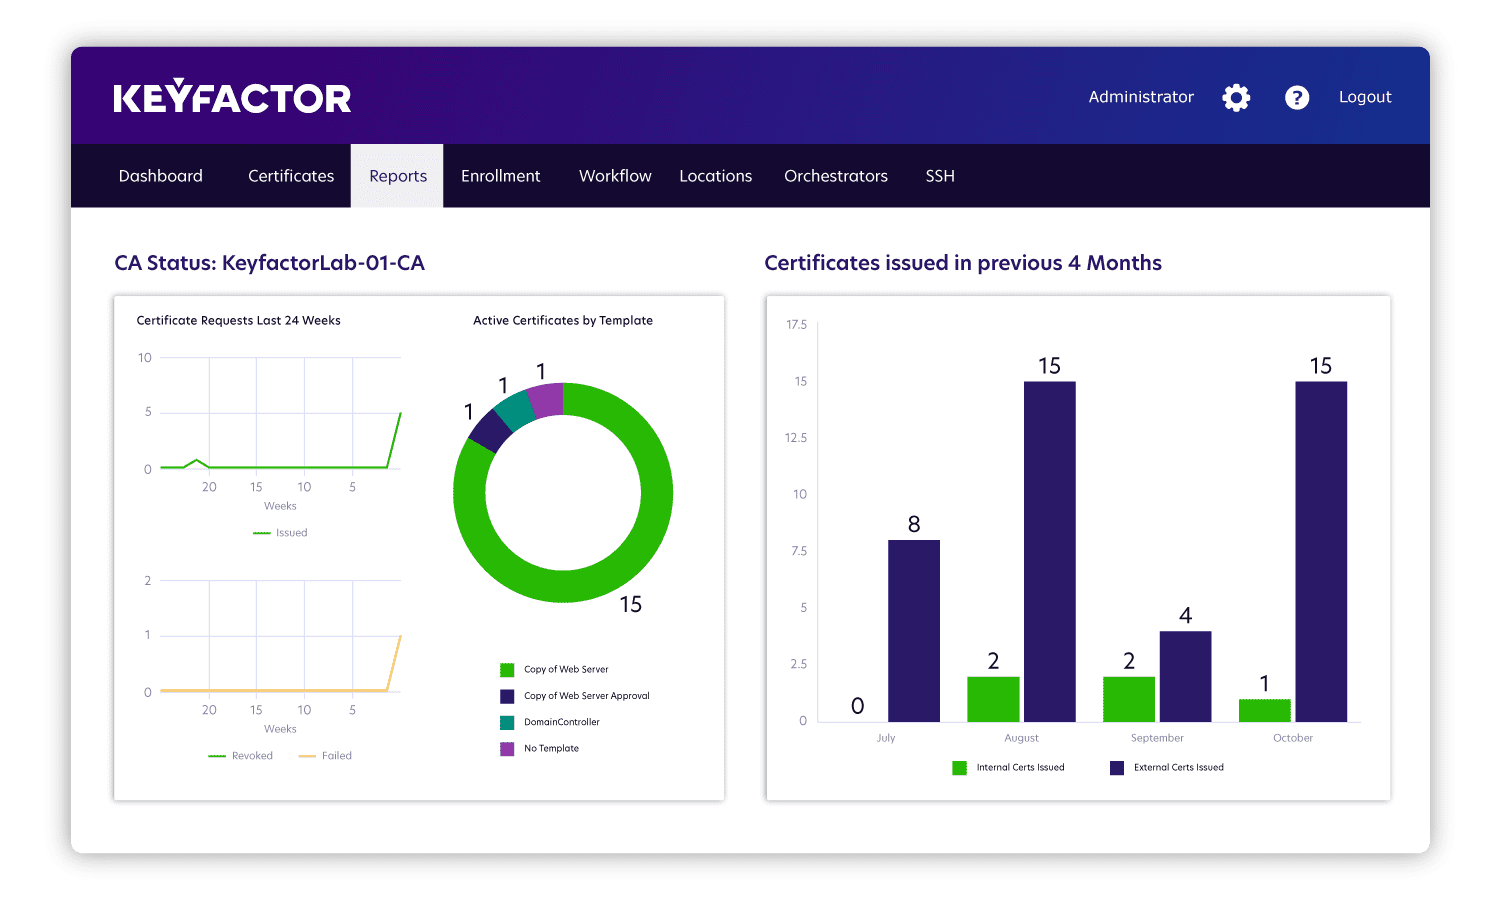
What to track: It’s essential to know all of the certificate authorities (CAs) your organization uses (both public and private) and to keep tabs on the certificates that they issue. Many teams are in charge of three to four public CAs that integrate across the entire company as well as an internal issuing CA. With all these CAs in play, you need an overview of activities at any time.
Why to track it: Visibility into CA issuance is important to detecting any unusual, ominous or hidden activity. For instance, one organization thought they had 1,000-2,000 certificates, but a Keyfactor inventory scan found more like 200,000 certificates. We discovered a server in the environment was rebooting every six hours, and whenever it rebooted, it requested a certificate — and this had gone on for two years without anyone noticing.
How to track it: A report can show you the number of certificates that each CA issues daily, providing visibility to pinpoint trends and get ahead of any issues. If your team expected to issue two or three certificates a day but then you see triple that activity, you can identify which CA is causing the spike and investigate further, since this could indicate malicious activity. Overall, seeing those spikes and anything else out of the ordinary is a great indicator that something might be wrong and warrants a closer look.
5) Solicitantes y propietarios de certificados
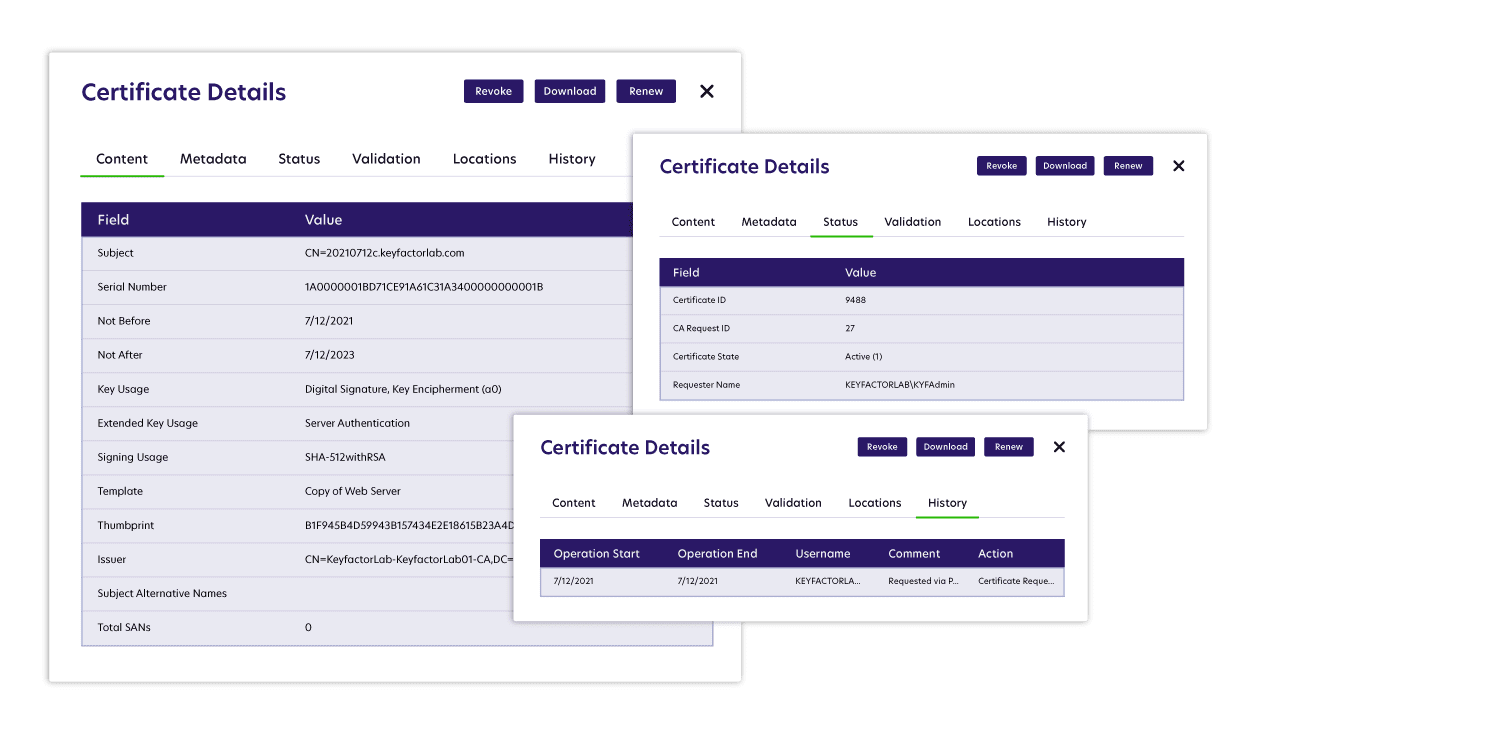
What to track: Next you need to know who is requesting certificates and who owns those certificates. Although this sounds simple, handing out certificates can get unwieldy very quickly, becoming like that classic Oprah moment “you get a car and you get a car!”
Why to track it: You need to know who requested a certificate and who owns it because when there’s a certificate expiration or operational downtime, you need to know who to go to for the renewal. Typically when outages happen it’s because someone wasn’t paying attention to a certificate or there was no renewal process in place.
And it only takes one certificate to cause an outage, such as the Microsoft Teams outage that happened shortly after COVID hit. It was just one certificate that expired, but it was a huge hit to Microsoft at a time when Zoom was starting to become dominant.
How to track it: The best way to track certificate requests and ownership is to introduce a report that offers a detailed view of who requested a certificate, who owns it, where it is and who to notify about an upcoming expiration and renewal.
6) Certificados autofirmados
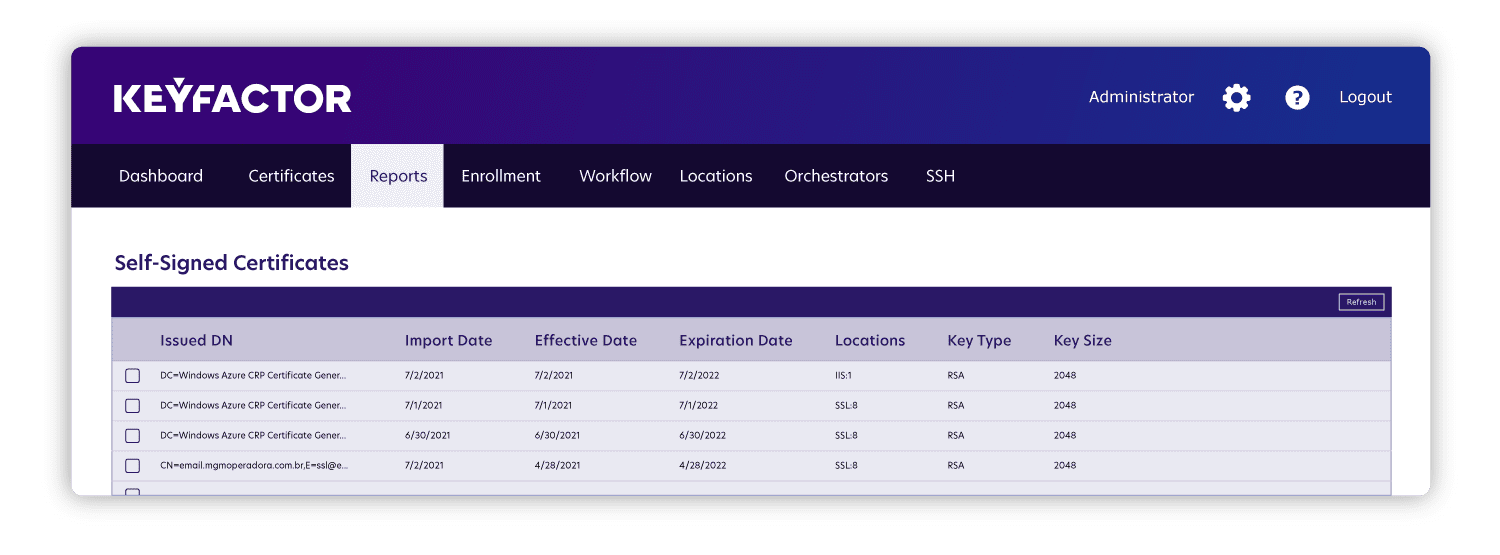
What to track: As DevOps teams grow, most organizations see a rapid increase in self-signed certificates put in place by the engineering team to keep up with the faster pace of development. A self-signed certificate is one that is not really public or private — it’s basically an onboard CA that’s attached to a certain tool, and it’s critical to understand where they exist.
Why to track it: Many organizations try to figure out how they can make self-signed certificates compliant with their PKI policy. Often they go about this by integrating their PKI program with HashiCorp Vault or a CA on their Istio service mesh. These integrations can get out of hand fast, but they do show exactly where the certificates are. Otherwise, security teams likely have limited to no visibility into where the engineering team issued self-signed certificates.
How to track it: This type of shadow IT primarily exists when certificates are cumbersome for developers to obtain. What you need is a report that shows who is going around your policies and when. Then you can use that insight to identify ways to improve your processes to make it easier for them to get certificates securely without slowing down their processes.
7) Certificados comodín
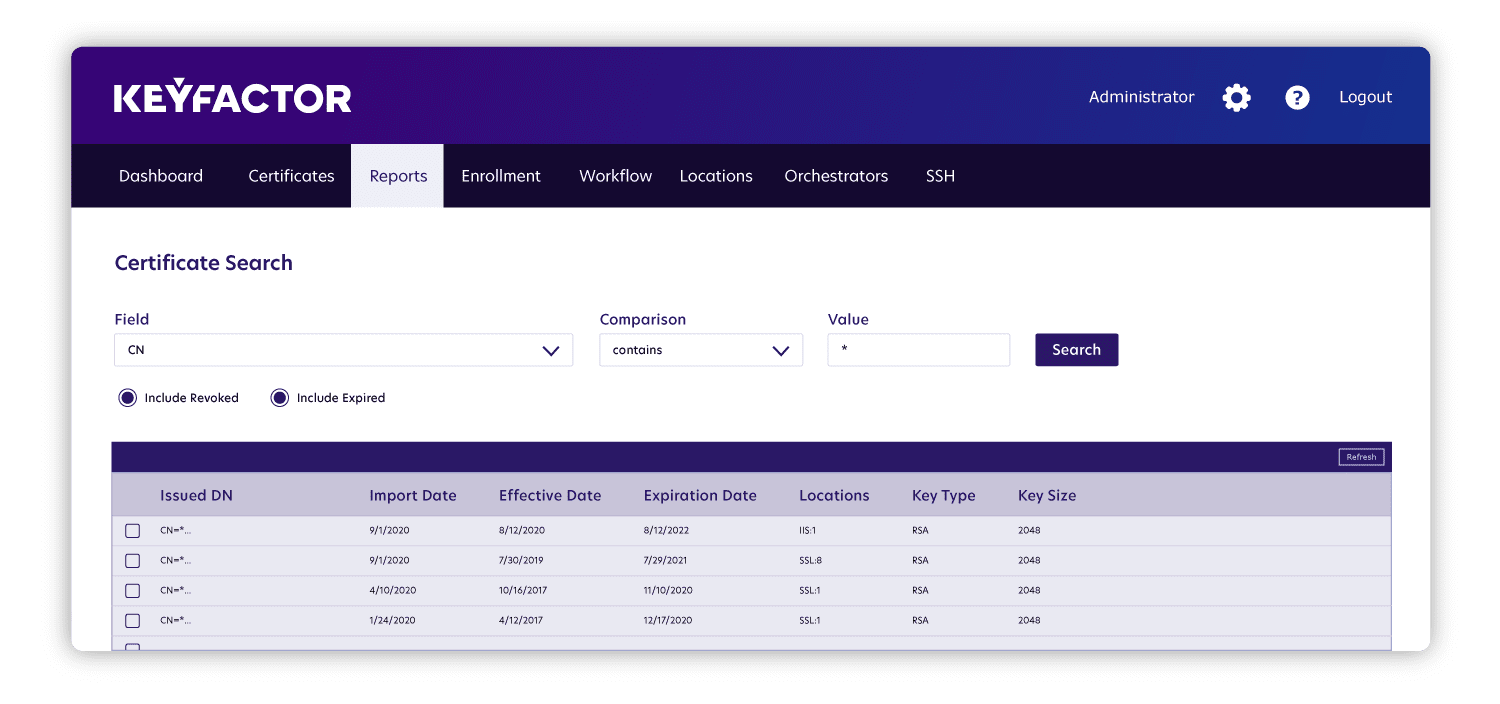
What to track: A wildcard certificate is a single certificate that’s used on multiple subdomains. They provide a lot of cost savings, but a single point of failure with the certificate can affect multiple areas of the business. This presents a huge risk in terms of outages and attacks.
Why to track it: If you don’t know which certificates are wildcards or if you don’t know every application using a certain wildcard certificate, you’re left with a blindspot. Specifically, if something goes wrong with that certificate or you need to renew it, you’ll have difficulty identifying everything that could be affected. This recently happened to Spotify, when the entire service went down because the team forgot to renew a TLS certificate that was a wildcard.
How to track it: You need a report that tells you which certificates are wildcards and the subdomains to which each one is attached. The best way to do this is to mark any wildcard certificates in a certain way, for example with an asterisk. Without this type of report, you might not know that a certificate is a wildcard. Or even if you do, you might not know every application consuming the certificate, and the only way to identify that is through manual network scans.
8) Certificados automatizados frente a manuales
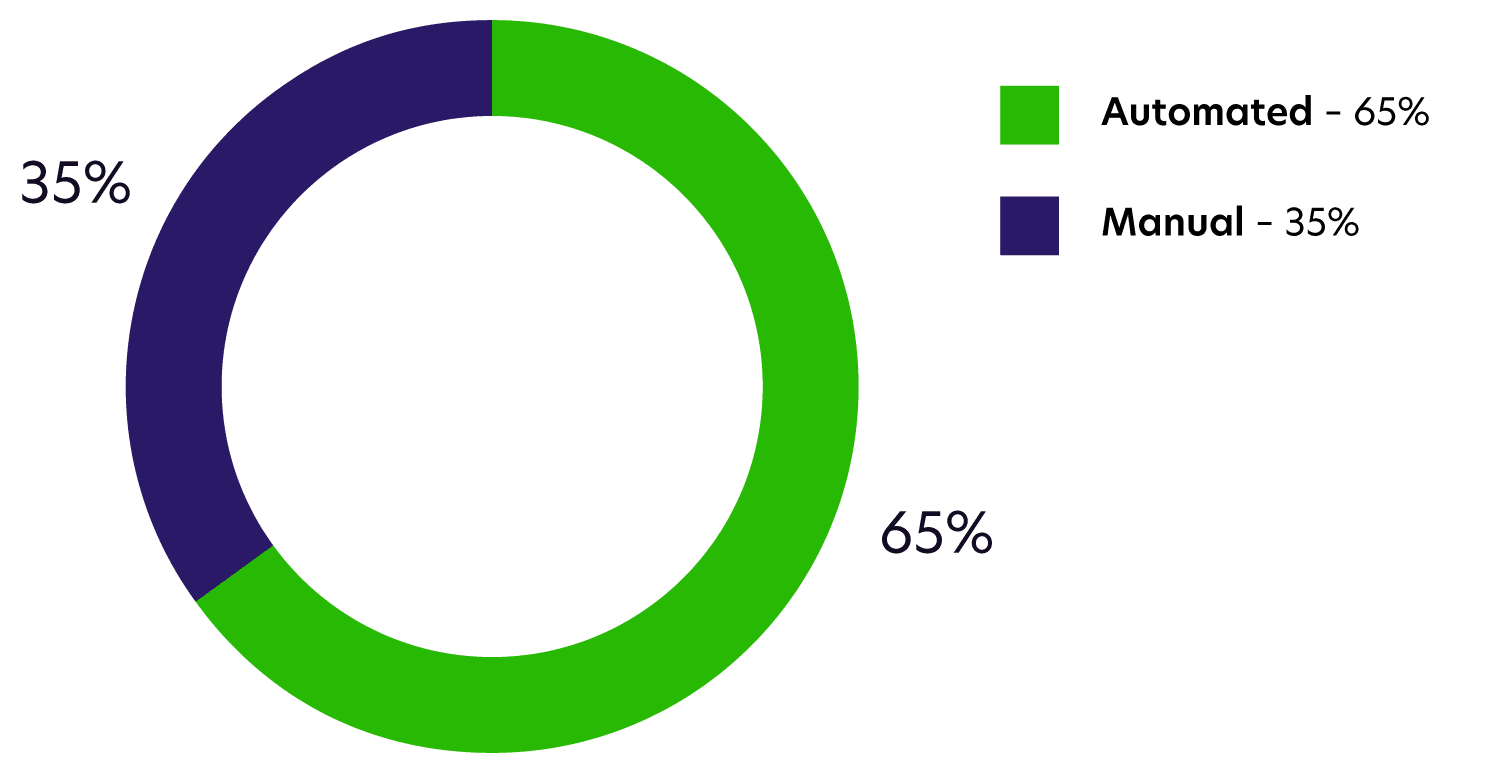
What to track: Which certificates have automated deployments and renewals and which certificates require manual updates? Generally, the more automation the better.
Why to track it: High automation allows for a more dynamic approach to your PKI operations and certificate management practices, whereas lower the automation leads to higher risk for outages. Further, automated certificates help with the default 90 day lifespan of certificates, as you don’t want someone to have to replace those certificates manually every 90 days.
How to track it: First you want a report that shows which certificates are automated and which are manual. Going one layer deeper, the nice thing about automation is that it will also create reports that show you how many certificates are getting renewed. This will display the lifecycle of certificates, so you can even get them replaced earlier than needed.
9) CRL Salud
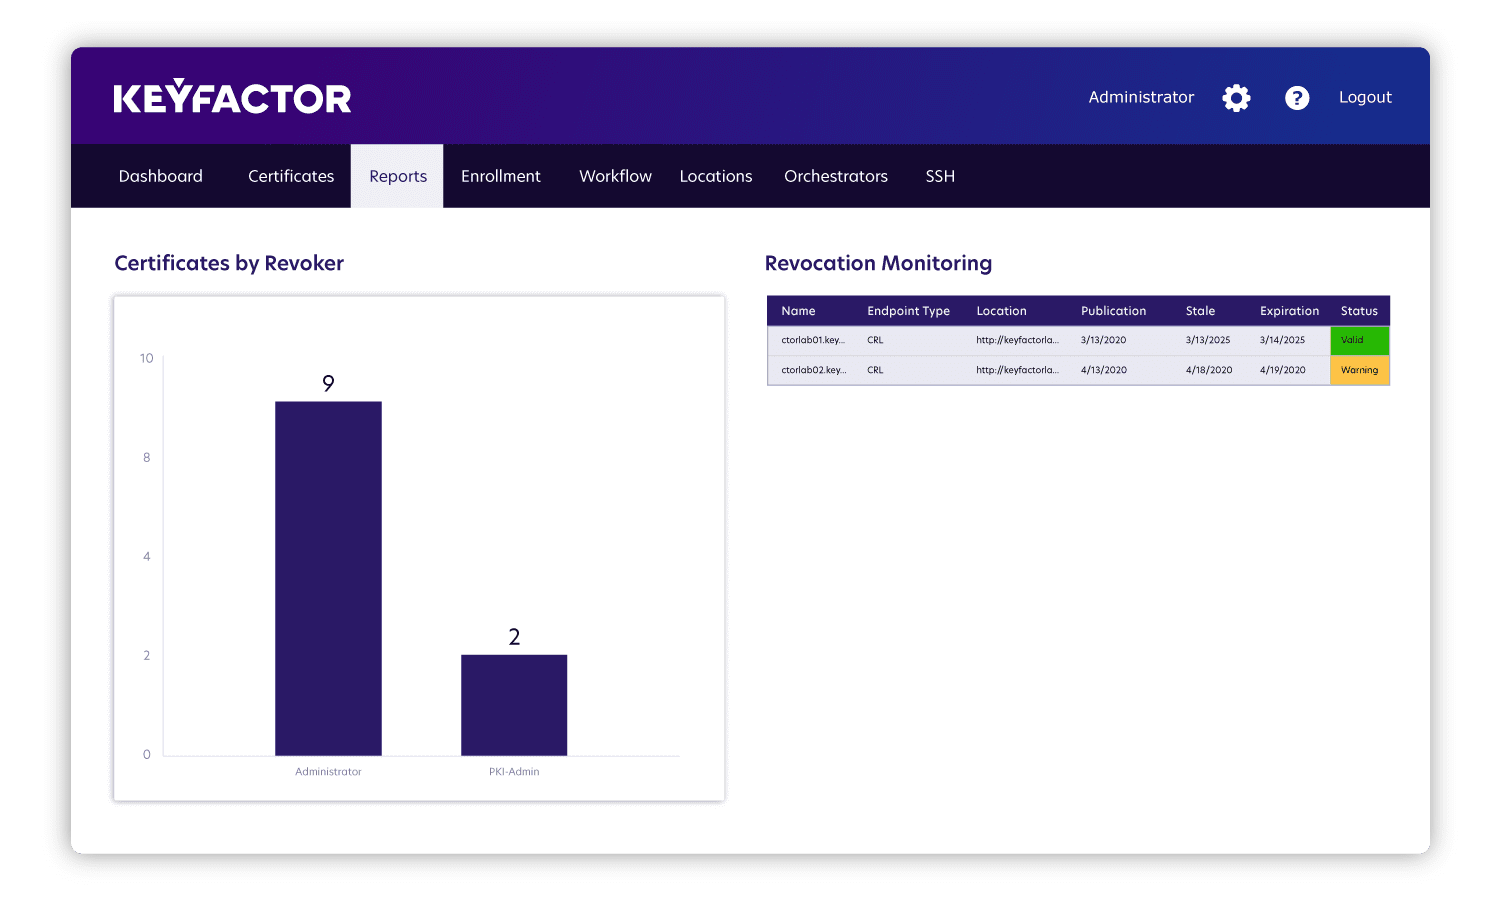
What to track: Certificate revocation lists (CRL) tell you whether or not a certificate is still valid, and they sit at the crux of PKI management. For example, if someone leaves your company, you might revoke their certificates, and a CRL makes that known so that others don’t trust those certificates anymore.
Why to track it: The CRL lives in a public place where anyone can check it. If for some reason a person or service can’t reach it, then they should not trust a certificate. So if the CRL is expired or unavailable, every certificate issued from that CA will be considered untrustworthy. As a result, CRL health is a single point of failure and needs monitoring.
How to track it: Introduce a report that shows which certificates have been revoked and add the ability to see who’s revoking those certificates. It’s important to note that certificates can be revoked for all kinds of reasons: They might be compromised, they might not be needed anymore or they might have been superseded.
10) Certificados desconocidos
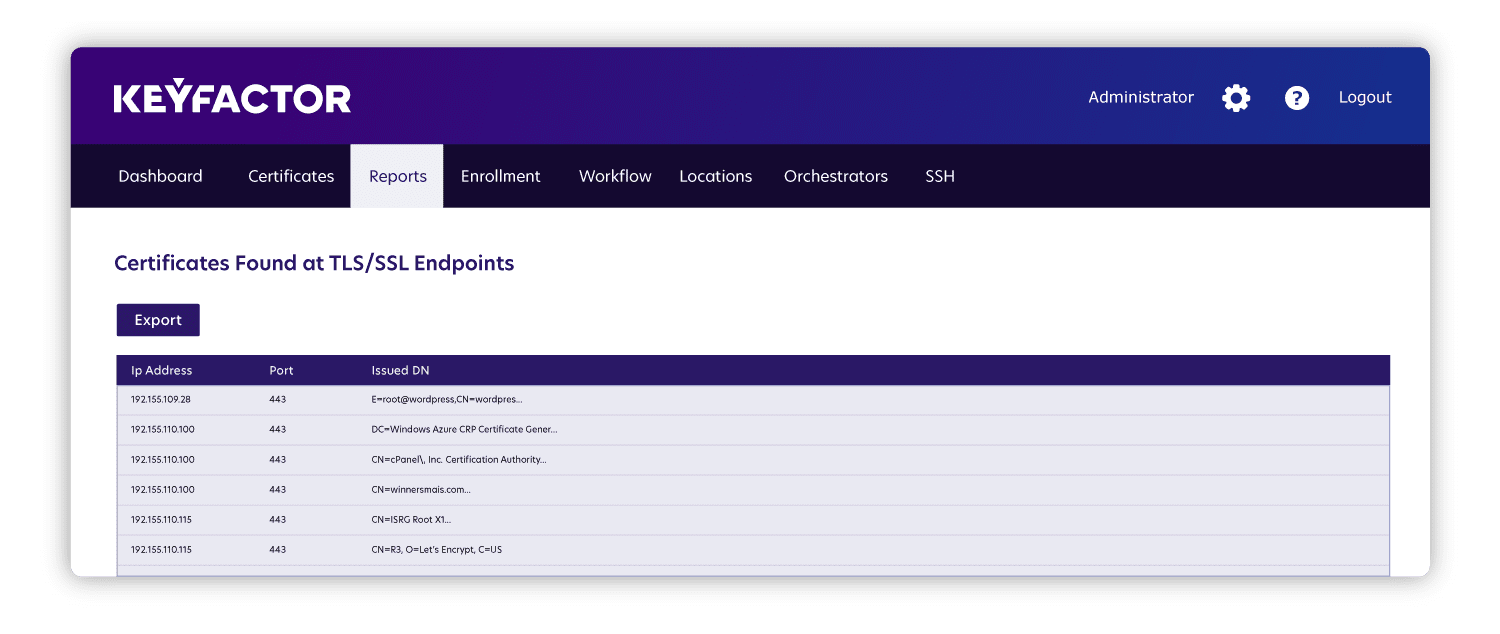
What to track: The previous metrics are all things that you can easily find by scanning your network or scanning different endpoints. The last one involves finding all of the certificates in your environment that you don’t know about, that way you can bring them into your database to eliminate blindspots and allow for reporting.
Why to track it: Before you can scan certificates to get specific information on them, you first have to know every single certificate that’s out there. What’s worse than not managing a known certificate is not managing an unknown certificate, and that makes it essential to have a complete inventory of all the certificates that exist.
How to track it: Scan your environment for all the ports that you have open that could be hosting certificates. If you know where certificate stores are, even if you just know the server name, you should be able to configure automation or an orchestrator to crawl that server and look for certificate stores. Then you can bring everything you find into one single database that you can report on. As you do so, look for things like a misspelling in your company name on a certificate, as that could be an indication of malicious activity.
Unirlo todo
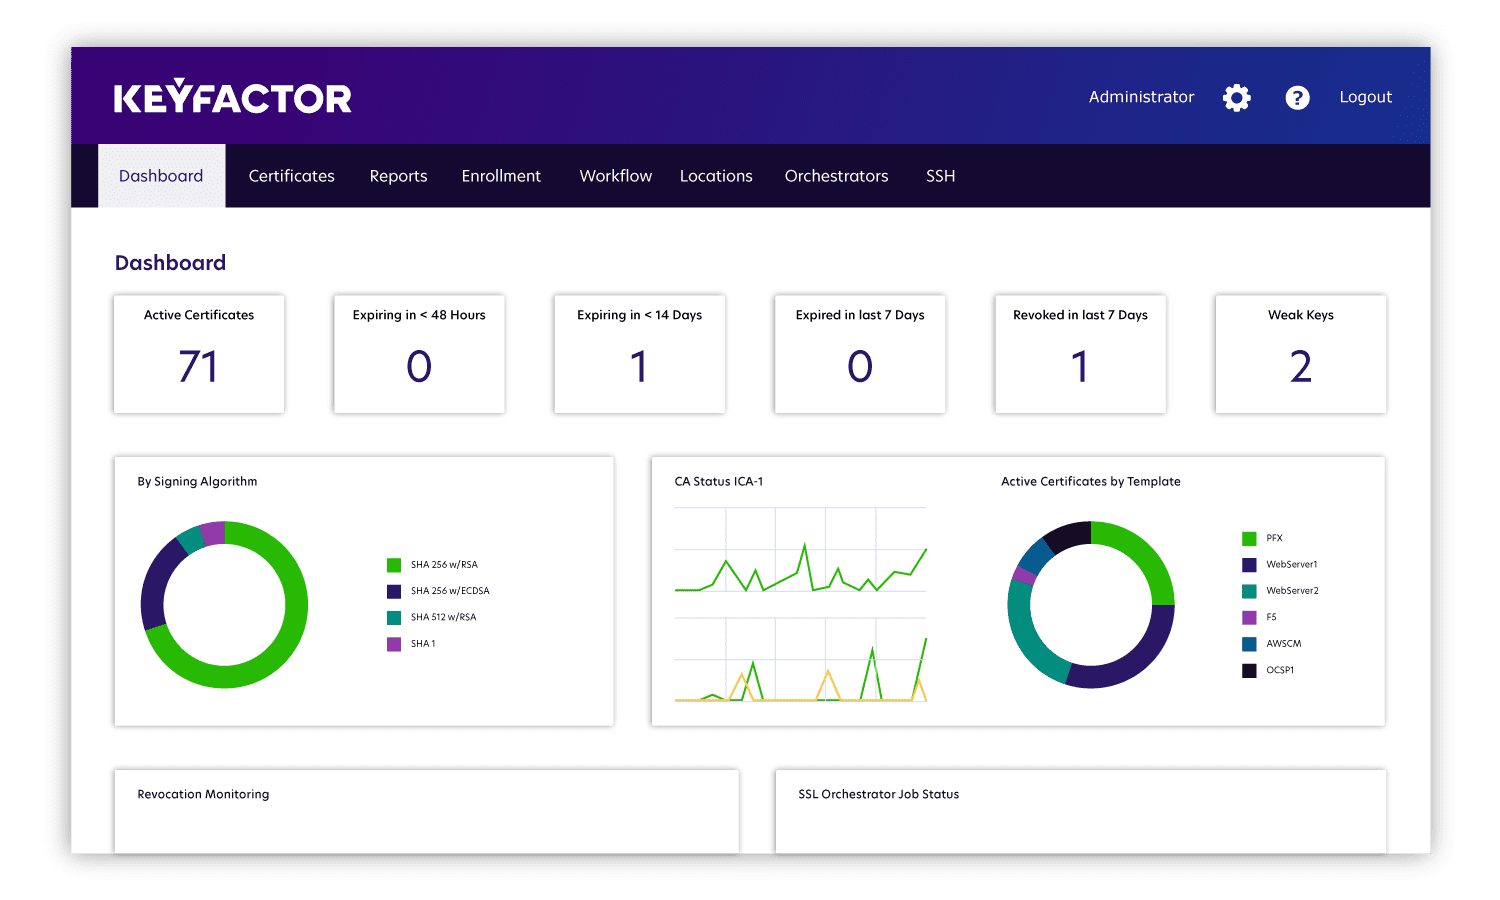
Aunque éstas son sólo diez de las muchas métricas de PKI que hay que controlar, juntas proporcionan una gran visibilidad que puede ayudar a su equipo a lograr la criptoagilidad. ¿Y ahora qué? Es hora de reunir todo para facilitar la visualización. Recomendamos empezar con los siguientes cuadros de mando:
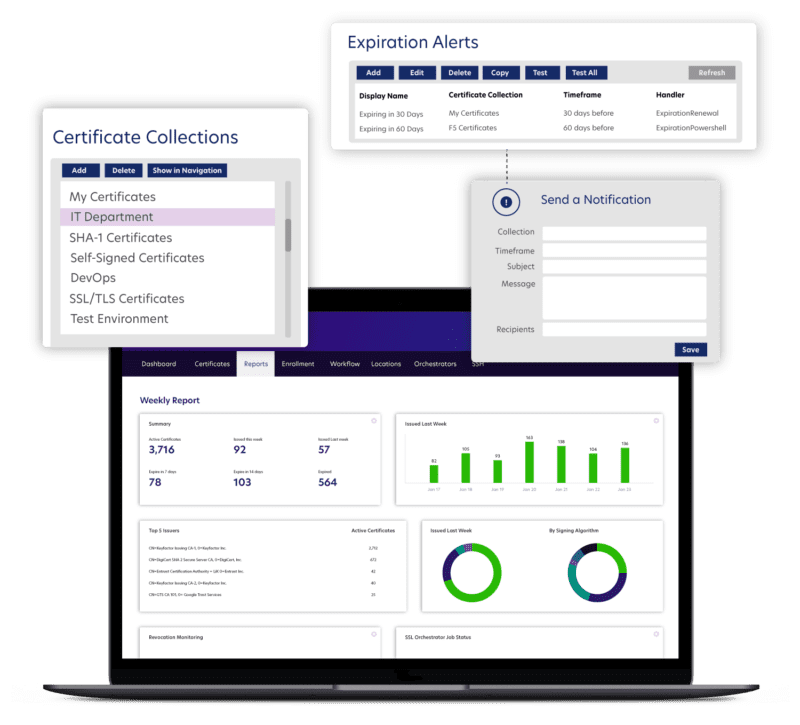
- Monthly Executive Report: Give executives a glance into issuance activity over the past month compared to the previous month. This provides a quick peek into the health of the CA, and it allows executives to quickly see if there are any red flags that need investigating (such as a large number of certificates set to expire in the next 2-4 weeks that could present a risk of outages). It also helps executives understand what to plan for when it comes to scaling the PKI architecture. For instance, do you need to stand up another issuing CA to take care of an increased load of certificates?
- PKI Status Report: Create a birds-eye view of PKI health metrics, like issuance, expirations, key strength and CA activity, for the more technically-minded executives. This gets into more detail while still providing an at-a-glance view of everything going on. It should also allow you to filter things like certificate collections by departments and to view or adjust expiration alerts. Overall, it provides a nice overview for a busy executive that understands the value certificates bring to the security of the organization and allows them to plan for improvements, like introducing more automation to reduce risk and free the security team’s time to focus less on renewals and more on value-add activities.
¿Le interesa saber más sobre por qué son tan importantes estas métricas y cómo empezar a realizar su seguimiento? Haga clic aquí para ver nuestro seminario web sobre las diez métricas PKI más importantes para obtener más detalles y consejos.
Suscríbase a The Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.