


Comment Keyfactor a amélioré la cybersécurité, l'agilité et l'évolutivité pour M&T Bank et EQ Bank
Banking and financial services data are among the most sensitive and confidential that an individual or an organization has. The industry must recognize the responsibility it has to its users, evaluate all potential cybersecurity weaknesses, correct any deficiencies, and remain vigilant on potential risks. Empowering security teams with strong, agile certificate management systems is essential for the growth of any financial organization, but what happens when that growth outpaces its team’s ability to manage certificates? MT&T Bank and EQ Bank turned to Keyfactor to unlock the answer to this question.
Moderniser les solutions de la MT&T Bank axées sur le client
M&T Bank is a community-driven bank headquartered in Buffalo, New York with over $155 billion in assets. Since its founding in 1856, the company has consistently delivered its clients’ community-driven solutions, which have naturally evolved over the last 165 years, just as M&T Bank has. Modern banking security requires agility and a commitment to improving its digital footprint, and M&T Bank has embraced the challenge.
Orienté vers l'avenir sans perturber le présent
M&T first modernized its public key infrastructure (PKI) in 2010, kicking off its engagement with Keyfactor, and the bank remains consistently dedicated to providing the most trustworthy and secure solutions for its users. The relationship with Keyfactor flourished further as M&T’s certificate volume for new devices and workloads began to increase rapidly.
Keyfactor Command
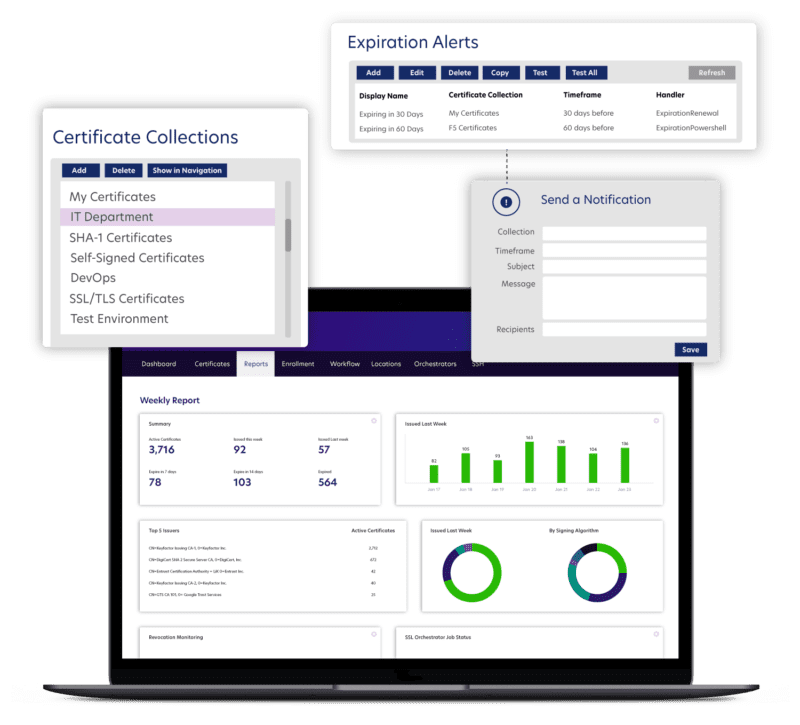
When M&T implemented Keyfactor Command in 2014, it provided its security teams with heightened visibility of their certificate inventory and created an alert system to remind users to renew expiring certificates. M&T upgraded these capabilities as Keyfactor Command evolved to include network discovery, APIs, and self-service enrollment.
Avantages d'une approche agile PKI
- Eliminated certificate blind spots: The cloud-based certificate monitoring and auditing solution provided M&T Banks with better visibility, allowing its cybersecurity teams to identify unauthorized certificates in their network. The comprehensive view of all active certificates, along with Keyfactor Orchestrator features like network scanning, allowed teams to locate certificates based on ownership, expiration, and location. Keyfactor helped M&T Bank locate and remove 50% of the self-signed certificates from their environment and significantly reduce their rates of error.
- Streamlined processes: M&T Bank has separate teams for administering externally trusted SSL/TLS certificates and the internal PKI. Although this is common in the industry, Keyfactor integrated with Entrust CA to give cybersecurity teams a seamless experience for certificate enrollment and lifecycle management. As a result, the cybersecurity team can organize certificates more effectively, notify application owners before their certificates expire, and tag each certificate with unique metadata, enhancing their capacity to track important information.
- Instead of running into policy barriers and chasing down developers and system administrators, M&T’s development and operations teams can issue certificates with ease by using the Keyfactor Swagger API interface.
- Improved scalability: The efficiency and scalability of Keyfactor Command has helped M&T Bank streamline its certificate management. The bank has more than 350,000 certificates, including certificates for auto-enrollment, mobile devices, web servers, networks, and cloud infrastructure.
Rationalisation du système bancaire de l'Equitable Bank basé sur l'informatique dématérialisée
Founded over 50 years ago, Equitable Bank manages more than $40 billion in assets while serving more than a quarter-million Canadians. Equitable Bank launched Canada’s first digital bank, EQ, Bank in 2016. By challenging the relevance of conventional brick-and-mortar banks, the branchless, entirely cloud-based EQ banking system grew dramatically, which raised internal questions about the stability of EQ’s infrastructure.
EQ ne disposait pas des processus et procédures nécessaires pour assurer le suivi des certificats. À l'exception de quelques feuilles de calcul, elle ne disposait d'aucun suivi interne des autorités de certification et dépendait principalement d'un mécanisme ad hoc qui permettait aux propriétaires d'applications de demander et d'émettre des certificats. Les équipes informatiques et d'infrastructure délivraient des certificats sans discernement dans les environnements de développement. Il était donc difficile pour EQ de fournir des rapports aux auditeurs internes et de maintenir l'intégrité des certificats délivrés dans l'ensemble de l'organisation. En l'absence d'un processus permettant de suivre la manière dont les équipes de l'organisation fournissaient les certificats, EQ a connu une augmentation des expirations de certificats non reconnues et non suivies. Chaque fois que cela s'est produit, l'application a été déstabilisée et des ressources importantes ont été détournées de leur flux de travail habituel pour résoudre la panne.
Centraliser les solutions
L'équipe chargée de l'infrastructure d'EQ avait besoin d'une solution offrant les capacités d'émission de certificats d'une autorité de certification interne solide, tout en éliminant l'effort de construction et de maintenance de cette dernière en interne. L'équipe de sécurité avait besoin d'une visibilité centralisée des certificats publics et privés pour superviser et gérer efficacement le parc informatique. Les administrateurs système et les programmeurs avaient besoin d'une méthode simple pour utiliser les certificats et communiquer avec les technologies DevOps automatisées comme Azure Key Vault, Kubernetes et Istio service mesh.
Only Keyfactor could fully manage and host a certificate authority and a full certificate lifecycle automation solution in a single cloud platform while delivering the most comprehensive set of APIs and integrations, allowing EQ’s DevOps teams to get started using them right away.
Améliorer les flux de travail grâce à la modernisation PKI
La mise en place de la nouvelle autorité de certification interne d'EQ était une priorité absolue. Avec le soutien de Keyfactor Command et Keyfactor PKIaaS, EQ a constaté des améliorations dans tous les domaines.
- Shifted PKI to the Cloud: Standardizing the issuance and provisioning of certificates allowed EQ to concentrate on proactive workflows, security, software delivery, and infrastructure domains while feeling confident that Keyfactor was looking after the PKI. Developers and engineers reduced the hours they normally spent seeking and deploying security-approved certificates to just a few minutes, thanks to DigiCert and the self-service Keyfactor Command.
- Gained complete visibility to remediate risk: Keyfactor provided full visibility of all active certificates by scanning the CA databases in DigiCert CertCentral and their current on-premise ADCS installation. This made it possible to find all internal and external certifications via the network. Security engineers no longer have to worry about misidentified, out-of-date, or questionable certificates that could jeopardize the availability of EQ’s apps thanks to a full inventory of certificates.
- Eliminate outages with automation: EQ successfully reduced the rate of human error and eliminated outages using a combination of expiration alerts and automated renewal workflows, saving its IT department from needlessly hiring two full-time team members to concentrate on manual certificate-related tasks like troubleshooting errors and resolving frequent outages. To automate the provisioning and renewal processes in an Azure Key Vault environment, Keyfactor specifically configured the Keyfactor Orchestrator. This automates the renewal process and replaces expired certificates with those from EQ’s updated PKI.
- Integrated certificate provisioning with DevOps workflows: The DevOps teams at EQ used Keyfactor’s extensive API and reference tools to connect with current infrastructure and toolkits. They authenticated all certificate-based identities to ensure safe and secure communications. The DevOps team automated the issuance and rotation of certificates for HTTPS encryption and ingress points across their deployments of Azure Kubernetes Service (AKS), Istio service mesh, and Docker containers using Keyfactor. The cumulative effect of these integrations improved agility and reduced downtime.
Sécuriser les secteurs bancaire et financier avec Keyfactor
Les équipes de cybersécurité de M&T Bank et d'EQ Bank peuvent plus facilement détecter et corriger les certificats potentiellement problématiques grâce à une meilleure visibilité des certificats, à des processus rationalisés, à une intégration stratégique et à une automatisation avec une mise à jour de PKI et de Keyfactor Command . Cela permet de renforcer la sécurité et de réduire le risque d'interruption de service. Plutôt que de s'attaquer hâtivement aux erreurs, les équipes peuvent se concentrer sur l'optimisation de l'expérience utilisateur.
Keyfactor understands just how high the stakes are in the financial industry when it comes to securing digital identity. Find out how the Keyfactor platform can modernize your PKI, prevent certificate outages, accelerate DevOps security, and more. Request a demo today.
S'abonner à La Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.