L'interopérabilité post-quantique en action : Comment la collaboration façonne l'avenir PQC de la cybersécurité




Note de la rédaction : Nous remercions tout particulièrement Tomas Gustavsson et David Hook, deux des plus grands experts de la cryptographie appliquée et de l'PKI, d'avoir rédigé ce blog. Les idées et la profondeur technique partagées ici sont le résultat direct de leur profonde expertise et de leur étroite collaboration.
À mesure que le paysage de la cryptographie post-quantique (PQC) évolue, une chose est claire : le succès ne viendra pas d'un travail isolé. L'interopérabilité - entre les algorithmes, les bibliothèques, les protocoles et l'infrastructure réelle - est essentielle pour rendre la PQC utilisable, fiable et sûre à grande échelle.
Chez Keyfactor, nous avons adopté une approche pratique de la CQP en testant et en contribuant activement à nos produits - en commençant par EJBCA, SignServer et Bouncy Castle - et en nous engageant avec l'écosystème plus large, y compris OpenSSL, CryptLib, WolfSSL, les vendeurs de modules de sécurité Hardware et les organismes de normes ouvertes tels que l'IETF, le NIST et X9.
Our goal is simple: demonstrate that post-quantum cryptography isn’t just a theoretical idea — it works. Today.
This isn’t just about us. It’s about collaboration — because when we test together, share results openly, and iterate with the community, everyone benefits.
Un laboratoire vivant pour l'interopérabilité des CQP
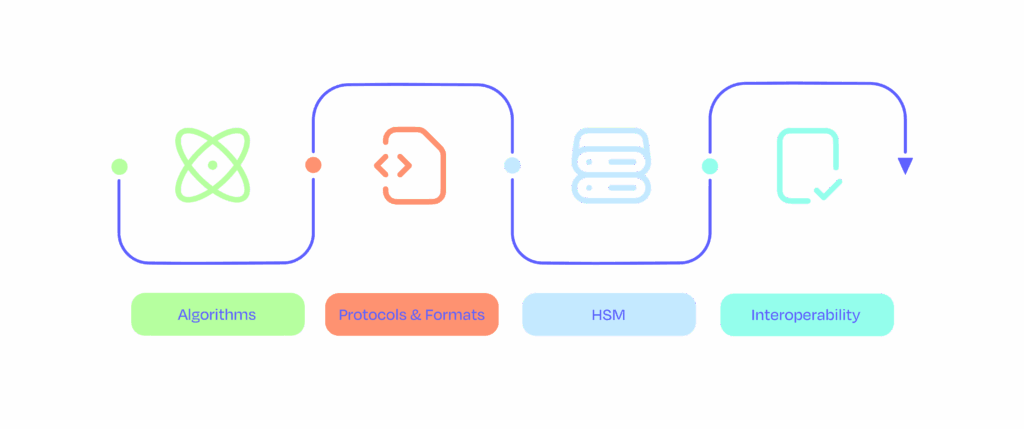
We maintain a living resource that documents real-world interoperability testing with PQC algorithms, protocols and formats across multiple tools and lifecycle stages. We want to share practical configurations and observations that reflect what’s actually needed to make PQC work in modern PKI and signing deployments.
Here’s a snapshot of what we’ve tested so far:
TLS 1.3 Authentication + Key Exchange
- Use Case: Mutual TLS (mTLS) with PQC certificates
- Tools: EJBCA + OpenSSL 3.5 + Bouncy Castle
- Outcome: Success using ML-DSA for authentication and ML-KEM for key exchange — a milestone toward crypto-agile secure communications.
CMS Signing and Validation
- Use Case: Code, container, and document signing with PQC
- Tools: SignServer, Bouncy Castle, OpenSSL
- Outcome: Cross-library verification of CMS-signed messages with ML-DSA and SLH-DSA. Encryption with ML-KEM also validated.
Issuing Certificates
- Use Case: Issue, renew and revoke PQC-enabled certs
- Tools: EJBCA, Bouncy Castle, OpenSSL
- Outcome: PQC CSRs generated and processed; Certificates, CRLs and OCSP responses validated across libraries.
Hybrid Certificates
- Use Case: Gradual migration using hybrid certs (e.g., ECDSA + ML-DSA)
- Tools: EJBCA, Bouncy Castle and WolfSSL
- Outcome: TLS with hybrid certificates is functioning today. Testing has been ongoing within X9.146. More testing underway for corner cases like dual-key storage and signture validation.
Hardware Security Modules (HSMs)
- Use Case: PQC key management in secure hardware
- Vendors: Securosys, Fortanix, Crypto4A, Utimaco and CryptoNext
- Outcome: Early success with LMS and ML-DSA support, with ongoing work to validate object size limits and integration edge cases.
La collaboration stimule l'innovation et les normes
This work is possible because of active collaboration between maintainers, implementers, and the broader open-source community. Participating in the IETF PQC Hackathon and contributing to ongoing ACVP testing allows us to catch bugs early, align on evolving drafts, and push forward on shared challenges — from signature size handling to private key, CMS and PKCS#12 encoding nuances.
These collaborations aren’t just technical. They help build trust, transparency, and alignment — essential ingredients when rolling out something as foundational as new cryptographic primitives.
Rejoignez le voyage - Essayez vous-même
If you’re working in PKI, signing, or security infrastructure, now’s the time to start experimenting with PQC. You don’t have to wait for final standards — protocols, formats and algorithm updates are stable, and libraries like Bouncy Castle and OpenSSL already support testable implementations.
We continuously update our Post-Quantum Cryptography (PQC) lab environment to support new use cases. Try it out today!
Explore our ongoing interoperability testing efforts on this page — we’ll keep it updated as we make progress: Interoperability and Future-Ready Cryptography
EJBCA, SignServer, and Bouncy Castle also maintain broader interoperability and certification coverage beyond just PQC — supporting your needs across current and future cryptographic standards.
EJBCA: https://docs.keyfactor.com/ejbca/latest/interoperability-and-certifications
SignServer: https://docs.keyfactor.com/signserver/latest/interoperability
Bouncy Castle: http://docs.keyfactor.com/bouncycastle/latest/interoperability
Ressources connexes
Pour en savoir plus sur les outils, les normes et la collaboration qui font progresser le CQP, consultez ces références clés :
IETF Hackathon – PQC Certificates: https://github.com/IETF-Hackathon/pqc-certificates?tab=readme-ov-file#ietf-hackathon—pqc-certificates
PQC Almanac: https://downloads.bouncycastle.org/java/docs/PQC-Almanac.pdf
Let’s make PQC not just ready — but usable, reliable, and trustworthy. Together.
S'abonner à La Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.
Lire la suite
Comment Keyfactor la résilience quantique grâce aux technologies Microsoft
En savoir plus
How Ready Is Your Cryptography, Really? Take the PQC Lab Assessment
En savoir plus