EJBCA SaaS PKI ist jetzt auf Microsoft Azure verfügbar



It’s no secret that organizations rely heavily on public key infrastructure (PKI) and machine identities to securely build, deliver, and run applications. Historically, Active Directory Certificate Services, also known as Microsoft CA, has been the de facto PKI choice for organizations — it’s well integrated into the Microsoft infrastructure and supports standard use cases.
However, as companies shift to hybrid and multi-cloud environments with Azure and Active Directory (AD), traditional on-premise Microsoft CAs simply cannot support their migration.
Traditional PKI wasn’t built to handle the volume and velocity of certificate usage today, which spans from web servers and load balancers to mobile and IoT devices, and increasingly, CI/CD tools and cloud-based infrastructure.
Plus, there are additional roadblocks for organizations to navigate:
- Operational challenges: Microsoft CA only allows one CA per server. At a time when organizations need to issue new certificates from a variety of CAs on a daily basis, this creates an overly complex footprint at scale.
- Limited integrations: While Microsoft CA integrates well with on-premise Microsoft infrastructure, that’s where it ends. This lack of integration support doesn’t work well as organizations move to a multi-cloud environment.
- Lack of support: Microsoft is well aware of these limitations and is no longer actively supporting or developing Microsoft CA, meaning that the gap between the limitations of the solution and modern use cases will only continue to widen.
- Lack of flexibility: Traditional PKI is rigid and inflexible. Organizations need a modern PKI solution that can be deployed how and where they need it, whether it’s on-premise or in the cloud, fully managed or self-hosted.
Without a cloud-based PKI, organizations struggle to stretch their existing PKI deployment during migration, often to its breaking point. The good news is there’s a clear path to a modern PKI in the cloud.
Modernisieren Sie Ihre PKI: Migrieren Sie zu Microsoft Azure mit EJBCA SaaS
Heute freuen wir uns, den neuesten Schritt von Keyfactorbei der Bereitstellung von Sicherheitslösungen bekannt zu geben, die Innovationen in modernen Unternehmensumgebungen vorantreiben - EJBCA SaaS auf Microsoft Azure.
EJBCA SaaS ist eine flexible, skalierbare und plattformunabhängige CA, die On-Prem-, Hybrid- und Multi-Cloud-PKI-Anwendungsfälle unterstützt. Sie ist im Azure Marketplace verfügbar und macht es Anwendern einfach, die Cloud-Migration durch die Authentifizierung digitaler Identitäten mit Cloud-nativer PKI sicher zu beschleunigen.
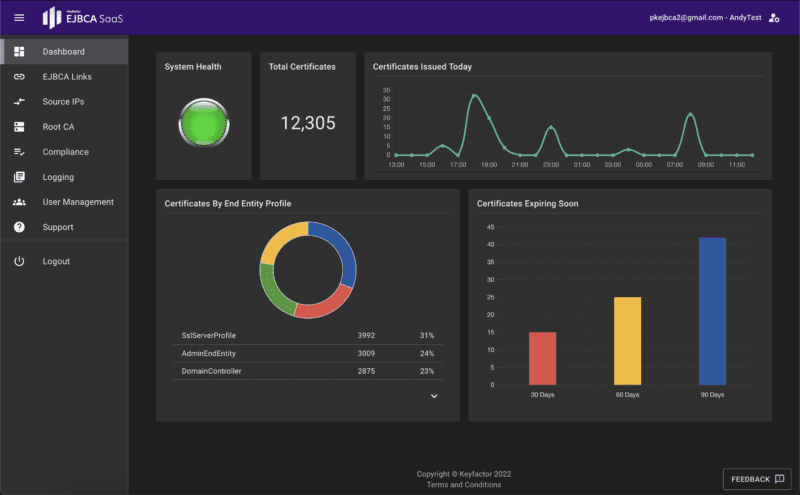
Die wichtigsten Merkmale und Vorteile sind:
- Simplify PKI: Reduce the effort and expense of deploying and maintaining PKI internally. Underlying CAs, HSMs, and infrastructure are hosted and managed by Keyfactor experts.
- Support any use case: Integrate with your existing Active Directory (AD) or Azure AD, and support any platform with multiple protocols and interfaces, including ACME, SCEP, EST, CMP, REST API, and more.
- Deploy fast, run anywhere: Deploy in virtually any Azure region in no time, with integrations to Azure Key Vault and Azure Managed HSMs for key protection.
- Scale on-demand: Meet increasing demands with an unlimited number of CAs, automated scaling, and support for high availability and redundancy — only paying for what you use.
- Self-service control: Manage and control your PKI from a single SaaS portal. Start and stop a dedicated root CA, add networks, configure logging, and more.
Möchten Sie mehr erfahren?
- Erfahren Sie mehr über EJBCA SaaS PKI
- Erste Schritte mit EJBCA SaaS auf Azure
- Registrieren Sie sich jetzt für unser kommendes Webinar, um eine Live-Demo von EJBCA SaaS auf Azure zu sehen.
Die Quelle abonnieren
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.