De Kuala Lumpur à Crypto-Agility : Réflexions sur la conférence PQC 2025 du PKI Consortium

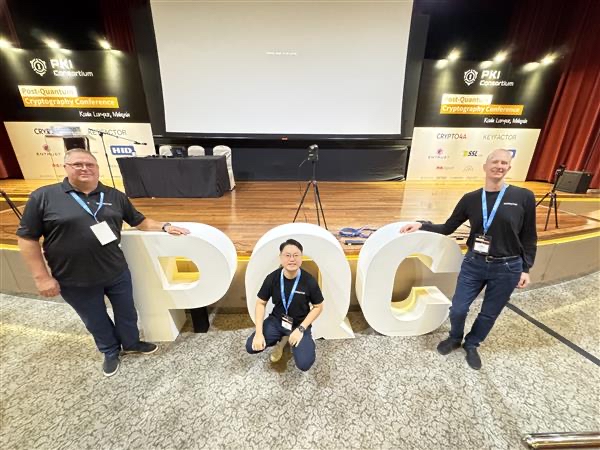



It is my favorite event that I look forward to all year: the PKI Consortium’s Post-Quantum Cryptography (PQC) Conference.
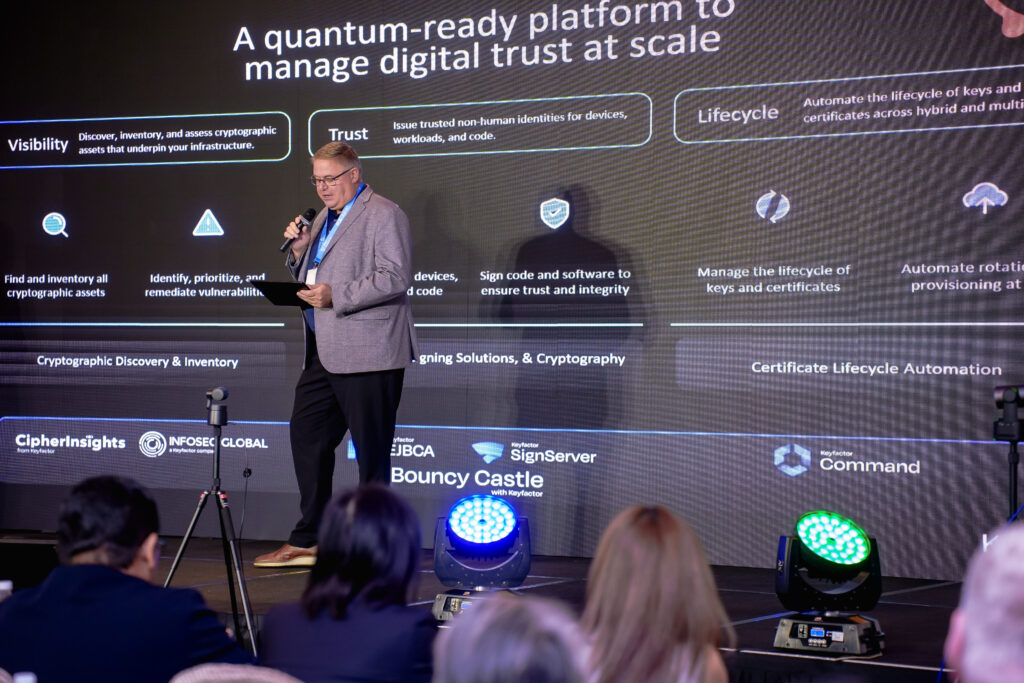
It is a place where technical leaders, from partners to competitors, come together to collaborate and innovate for the sake of digital trust, and 2025 certainly did not disappoint.
Adding to the general excitement, this year’s event, held in Kuala Lumpur, coincided with a quantum leap in Malaysia’s cybersecurity readiness:
- The Ministry of Digital and the National Cyber Security Agency (NACSA) launched the National Post-Quantum Cryptography Readiness Roadmap.
- This framework will strengthen both national and ASEAN-wide resilience against quantum threats, aligning with Forrester’s 2026 Asia Pacific Predictions Report’s forecast that quantum security will become a strategic priority for more than 90% of enterprises in the region.
- Attendees heard about this significant development firsthand from Tuan Fabian Bigar, Secretary General of the Ministry of Digital, during his keynote presentation, where he emphasized that PQC is a shared opportunity for us to shape a quantum-secure world.
And he could not be more right: We must work together to accelerate digital trust and prepare organizations for a post-quantum future now before it is too late.
That’s why I’ve pulled together key takeaways and personal reflections from the event so that whether or not you were able to attend, you have the critical information you need to move forward.
PQC : La conversation s'est déplacée
A year ago, PQC discussions were deeply technical:
- Which algorithms will NIST finalize? What will they mean for my business?
- When will FIPS certifications catch up?
- How will hybrid and composite approaches actually work?
Cette année a été complètement différente.
The focus has moved from theory to implementation.
Now, the questions sound more like:
- How do I get started without overhauling everything at once?
- What’s the first step to becoming quantum-ready?
- How do I measure and sustain progress?
A memorable quote from the conference neatly summarizes the shift in attitude:
“PQC adoption is not a project; it’s a program. It does not have a start and stop date. It will continue to be ongoing over a long period of time.”
I could not have said it better myself.
Niveaux de maturité : Comment définir la notion de "prêt pour le quantum" ?
Following this shift from algorithms to actions, the PKI Consortium PQC Working Group introduced something that will make a real difference: the Post-Quantum Cryptography Maturity Model.
This model builds on the PQC Capability Matrix but focuses less on products and more on organizational maturity. It helps answer questions like:
- What does “quantum-ready” actually mean?
- How can we benchmark progress across teams or business units?
- What should vendors and customers expect from each other?
This framework gives us a shared language for progress.
It is open for community feedback, and I strongly recommend you offer your insights (should you have any) because, as mentioned, it takes a village to build a quantum-safe future.
👉 Share your thoughts on the PQC Maturity Model here.
Les points clés à connaître
Voici les principaux éléments qui se sont dégagés des sessions formelles et des conversations informelles qui ont eu lieu entre les deux.
> La crypto-agilité est la seule véritable stratégie
If you build crypto-agility properly, you can adapt no matter what algorithm or vendor wins out.
Crypto-agility isn’t about guessing the right standard. It’s about preparing for constant change, whether it’s PQC, AI-driven threats, shorter TLS certificate lifespans, or new compliance rules like DORA, PCI DSS, or OCC guidance.
> L'PKI hybride continue de semer la confusion
There’s still a lot of uncertainty around hybrid approaches (combining classical and PQC algorithms).
And it is slowing people down. Here’s the quick and easy:
- Use hybrid PKI where it makes sense, particularly where certification or hardware support lags.
- But don’t let it become an excuse to delay progress.
- Les déploiements "purement PQC" sont aujourd'hui viables pour de nombreux systèmes internes et backend.
> La découverte est la ligne de départ
Almost every attendee I spoke to — regardless of their industry — had the same first question:
“Where do we start?” With discovery and inventory.
Je l'ai déjà dit et je le répète : On ne peut pas protéger ce que l'on ne voit pas.
Savoir où se trouvent les actifs cryptographiques - certificats, clés, algorithmes - est le premier pas vers un changement significatif.
> Conformité et résilience sont désormais indissociables
Compliance is no longer a box to check. It’s about building resilience so you can adjust quickly and efficiently when regulations or standards change.
La conformité consiste à se conformer à la barre. La résilience consiste à être prêt lorsque la barre se déplace.
> L'automatisation est un héros discret
The same automation practices that shortened TLS certificate lifecycles are now powering PQC migrations.
By reusing automation pipelines, organizations can save time and funding, while aligning two major initiatives under one modernization effort. Really, it’s a win-win.
Les 5 mesures à prendre dès maintenant
If the conversation has shifted from theory to action, then what should organizations actually do? Here’s how I’d frame it:
1. Start with discovery
Visibility is essential. Inventory every key, certificate, and cryptographic dependency across your infrastructure.
2. Assess and prioritize
Identify which systems matter most to your business. Start where the impact or risk is highest.
3. Automate where possible
Automation will reduce human error and speed up change. If you already have automation in place for certificate lifecycle management, you’re ahead of the curve.
4. Build crypto-agility into every decision
Crypto-agility creates flexibility across your entire security ecosystem. When you evaluate a new tool or service, ask: Can it adapt when policies, regulations, or technologies shift?
If the answer is no, you’re locking in tomorrow’s technical debt today.
5. Engage and collaborate
This is not a solo journey. Engage with communities like the PKI Consortium, share lessons learned, and help shape the standards that will define the next decade of digital trust.
Regarder vers l'avenir : De Kuala Lumpur à l'Allemagne
As I left Kuala Lumpur (with a few extra hours of jet lag and a lot of notes), one thought stuck with me:
We’re no longer asking if quantum computing will disrupt digital trust, but how ready we’ll be when it does.
So, here’s my challenge to every security leader reading this:
Between now and the next PQC Conference in Germany, how much closer will you be to crypto-agility?
Start small. Start now. Start with discovery.
Learn how Keyfactor can help you discover and manage cryptographic assets — the foundation for your improved crypto-agility.
S'abonner à La Source
Stay secure with Keyfactor's monthly newsletter, packed with expert insights and practical steps for quantum-readiness.