Keyfactor Tech Days 2027 – Be Part of The Trust Security Conference in San Diego Register now!
Post-Quantum Resilience for Financial Services

Quantum will break today’s encryption.
Get a clear path to resilience.

NIST’s post-quantum standards are final and “harvest now, decrypt later” attacks are already underway. Keyfactor helps you see your quantum-vulnerable cryptography and build the cryptographic-agility to migrate, without ripping out what you already have.
  • Book your 30 min quantum-readiness demo today and see your cryptographic estate and a prioritized path to post-quantum resilience.

Request a demo

Trusted by 40% of fortune 500
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo
Client Logo

Why post-quantum, why now

The standards are set and the clock has started. With NIST’s post-quantum algorithms now final, resilience is no longer a future question and it starts with a problem you may already have: if you can’t see your own cryptography, you can’t migrate it.

55%

of organizations lack full cryptographic visibility — the first blocker to post-quantum migration.

2030

the projected timeline for quantum to threaten today’s encryption (“Q-day”).

Today

long-life financial data is already being harvested now to decrypt once quantum arrives.

Why financial services isn’t quantum-ready

You can’t protect what you can’t see

Without a full cryptographic inventory, you can’t find your quantum-vulnerable algorithms, let alone prioritize which to migrate first.

Fragmented PKI can’t migrate at scale

Post-quantum means re-issuing and re-keying across every system. Siloed CAs and manual workflows can’t keep pace — and can’t evidence the change to auditors.

Regulators are already moving

NIST has finalized its post-quantum standards, and DORA and NIS2 now demand provable cryptographic-agility. Quantum readiness is a compliance and resilience mandate, not a future project.

How Keyfactor gets you quantum-ready

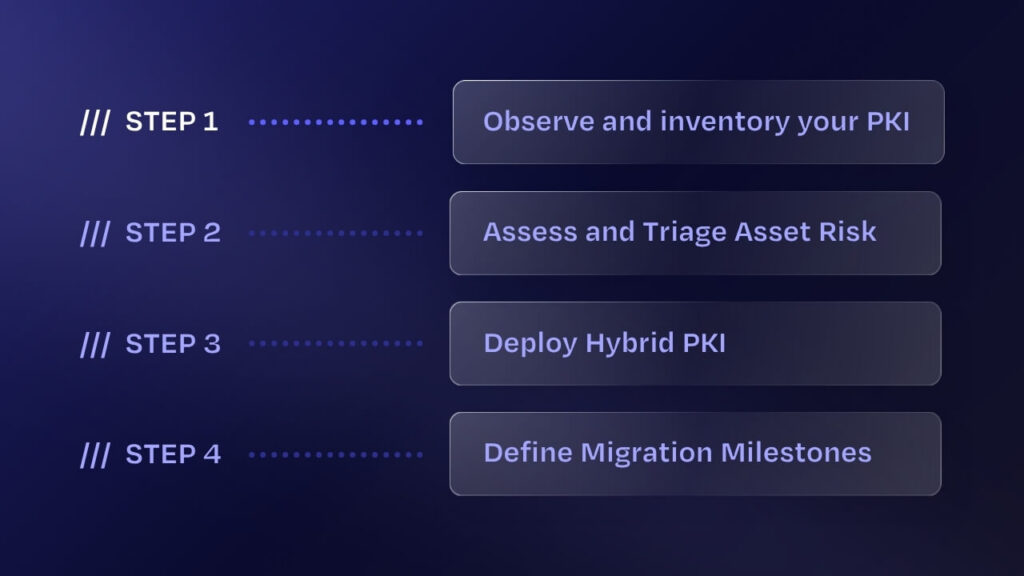
Keyfactor gives you one platform to discover, automate and prove your post-quantum migration — working with every CA, protocol and environment, no rip-and-replace required.
Continuous cryptographic discovery finds every certificate, key and algorithm across cloud and on-prem so you know exactly what’s quantum-vulnerable.
Automate the certificate lifecycle and swap algorithms from a single control point, so you can migrate to post-quantum cryptography without re-architecting your systems.
Governance, policy enforcement and audit logging make your post-quantum resilience demonstrable to regulators under DORA, NIS2 and PCI — reports in minutes, not weeks.

Continuous cryptographic discovery finds every certificate, key and algorithm across cloud and on-prem so you know exactly what’s quantum-vulnerable.

Automate the certificate lifecycle and swap algorithms from a single control point, so you can migrate to post-quantum cryptography without re-architecting your systems.

Governance, policy enforcement and audit logging make your post-quantum resilience demonstrable to regulators under DORA, NIS2 and PCI — reports in minutes, not weeks.

Resilience is a business decision, not just a technical one

Keyfactor gives you one platform to discover, automate and prove your post-quantum migration — working with every CA, protocol and environment, no rip-and-replace required.
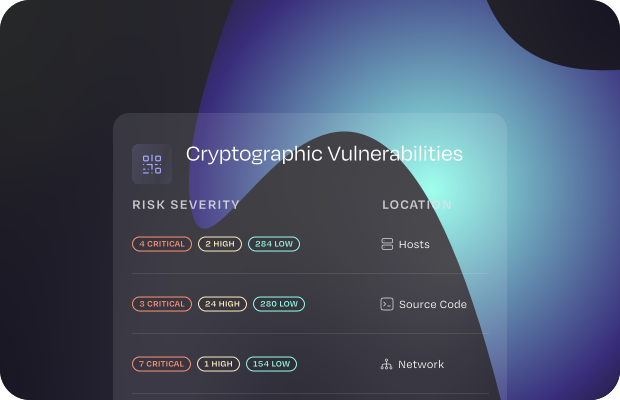
Automated cryptographic-agility prevents the outages and emergency migrations that disrupt digital financial services.
Demonstrate provable cryptographic-agility for DORA, NIS2 and PCI — before it becomes an audit finding.
A phased, prioritized path your board can approve and track, with progress you can evidence.

Automated cryptographic-agility prevents the outages and emergency migrations that disrupt digital financial services.

Demonstrate provable cryptographic-agility for DORA, NIS2 and PCI — before it becomes an audit finding.

A phased, prioritized path your board can approve and track, with progress you can evidence.

Proven in financial services

Cryptographic-agility is the foundation of post-quantum resilience and business continuity. See how leading financial institutions built it with Keyfactor — protecting uptime, customer trust and compliance.

Certificates would expire, but we wouldn’t know until systems went down. Since deploying Keyfactor, we’ve eliminated these incidents entirely.
David Yu VP Security Architecture, EQ Bank
EQ Bank sign at their headquarters in Toronto, Canada.

M&T Bank achieved secure cryptographic-agility with certificate lifecycle automation — the foundation for post-quantum migration.
Fred Cohn Digital Risk Leader, IoT Practice, Schneider Electric
Keyfactor X MT Bank Thumbnail LOGO