AI Identity: Why Every AI Agent Needs a Verifiable Digital Identity


DEFINITION
AI identity is a verifiable representation of an AI agent that establishes who or what the agent is within a digital environment. It enables systems to authenticate the agent, determine its authorized permissions and actions, and associate those actions with a trusted entity. AI identity provides the foundation for accountability, governance, and revocation, allowing autonomous agents to operate securely within enterprise systems.
Autonomous systems are becoming active participants in enterprise environments, making decisions and taking actions that can affect data, infrastructure, and business operations. Unlike traditional software, AI agents can dynamically interpret instructions, access systems, interact with other agents, and operate with a high degree of independence. Organizations therefore need a reliable way to know which agent is acting, what the agent is authorized to do, and whether the organization can trust the actions of the agent. A verifiable identity provides the foundation for authentication, authorization, accountability, and revocation, enabling organizations to securely deploy AI at scale. Without it, autonomous agents become powerful but largely ungoverned actors operating within trusted networks, increasing the risk of misuse, compromise, and unintended consequences.
AI has entered the trust era
The question organizations ask about AI has changed. It is no longer “what can it do?” The question now is “who is it?”
AI agents have quickly moved beyond generating responses to prompts. They now sense their environments, make autonomous judgments, and take actions across enterprise systems, such as initiating workflows, accessing sensitive databases, calling APIs, and coordinating with other agents at machine speed. This shift from automation to autonomy is not incremental. Automated systems follow instructions. Agentic systems interpret them. Automated systems operate within static boundaries. Agentic systems dynamically cross them.
That distinction matters because it fundamentally changes the nature of risk. In Keyfactor’s AI identity survey, 69% of cybersecurity professionals said vulnerabilities in AI agents pose a greater threat to their security and identity systems than human misuse of AI. Only 28% believe they could stop a rogue AI agent before damage occurs, and 86% agree that AI agents cannot be fully trusted without unique, dynamic digital identities.
The gap between AI deployment speed and identity readiness is widening. Organizations are deploying AI agents into production environments while still relying on identity models designed for humans and predictable applications. The result is a growing category of autonomous actors operating inside trusted enterprise boundaries without the identity controls to match their capabilities.
Identity is the dividing line between AI innovation and AI risk. It is the foundational control plane that determines whether autonomous agents can be authenticated, authorized, tracked, and revoked. Without it, every other security control becomes weaker.
What is AI identity and why does it matter?
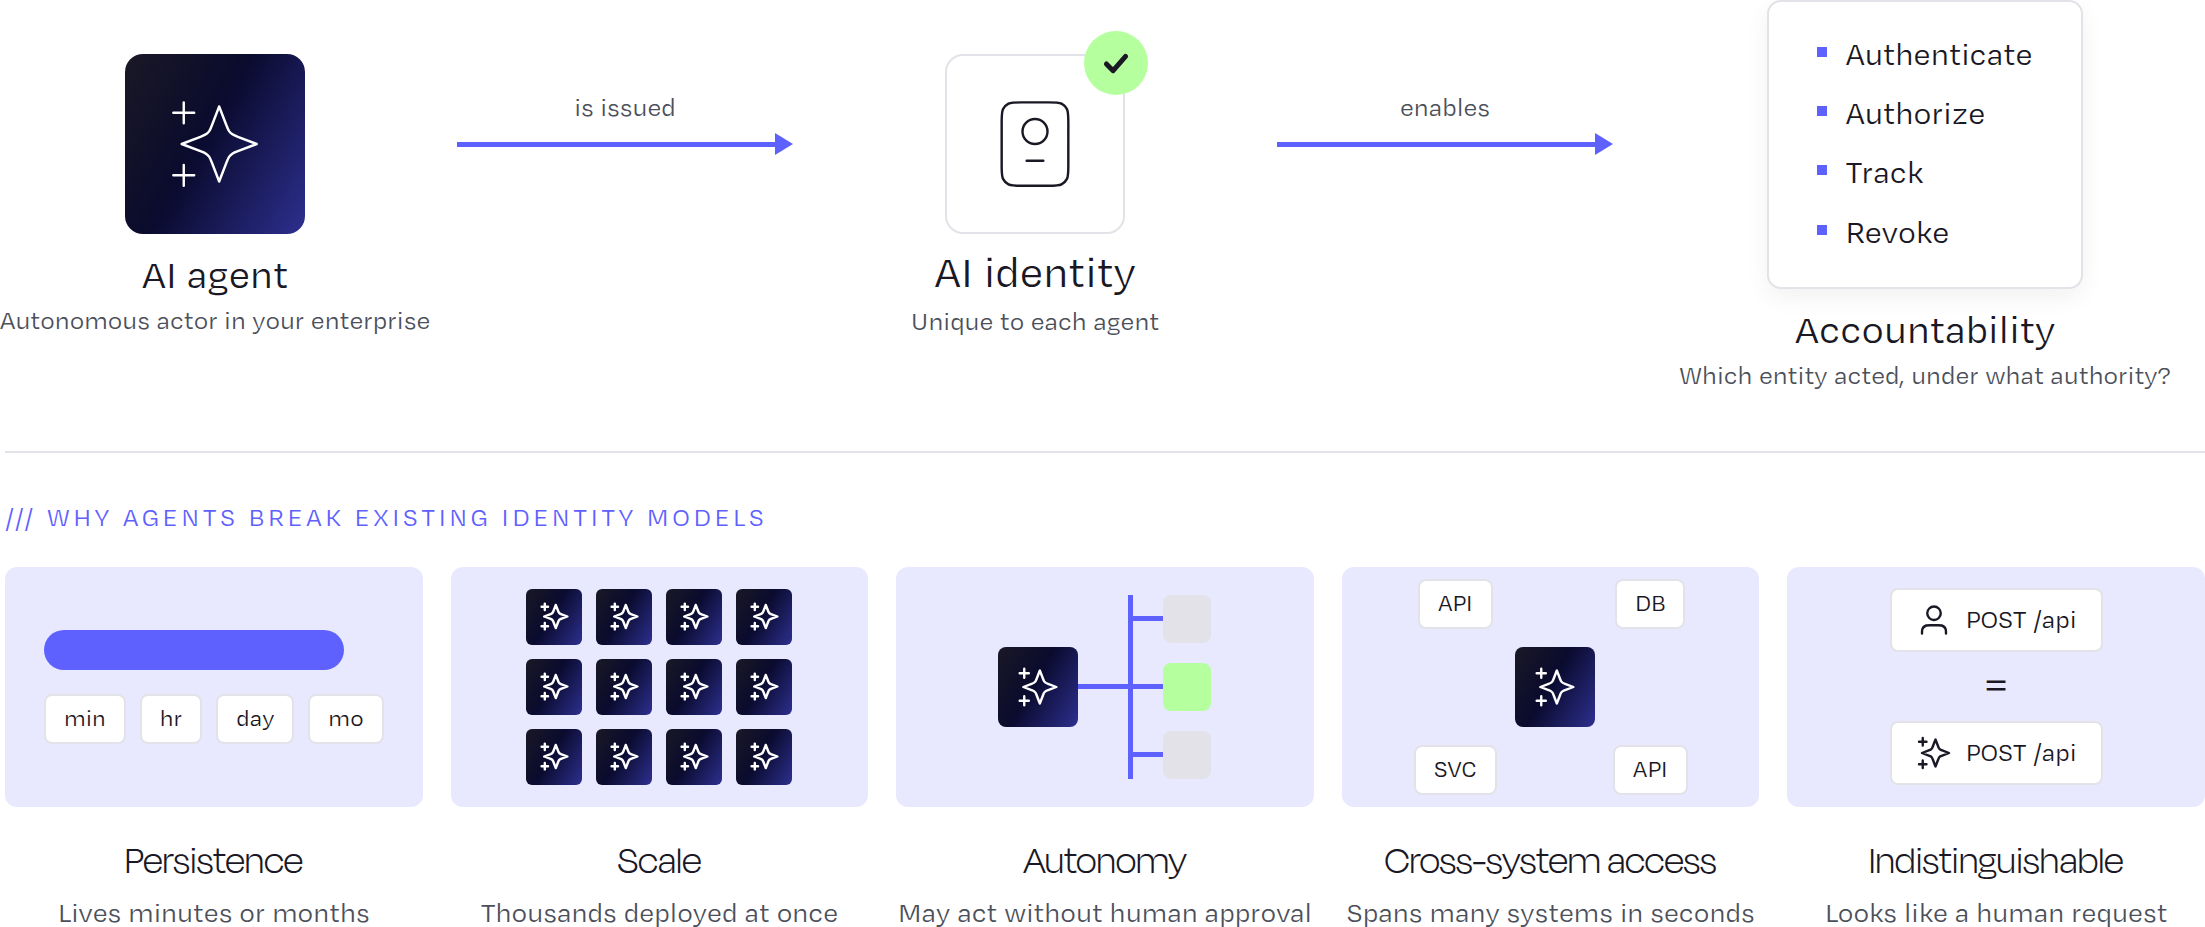
AI identity provides the ability to uniquely authenticate, authorize, track, and revoke an autonomous agent’s access and actions. It allows to answer the most basic security question about any actor in an enterprise environment: which entity did this, and under what authority?
AI agents do not fit existing identity models designed for human users or traditional applications. They introduce characteristics that make identity both more critical and more difficult to manage:
- Persistence with dynamism. AI agents may be long-lived services or ephemeral workers that exist for minutes. Some persist across sessions, accumulating context and authority over time. Teams spin up others for a single task and immediately decommission them. Identity models must accommodate both patterns.
- Scale. Organizations may deploy hundreds or thousands of AI agents simultaneously across different workflows, creating identity management challenges that dwarf anything in traditional user-centric systems.
- Autonomy. Agents make real-time decisions without human oversight. They do not wait for approval before acting, and their value lies in adaptability. This is the very trait that security systems often flag as suspicious.
- Cross-system access. A single agent might interact with multiple APIs, databases, and services in the course of a single task. Unlike a human user who typically works within a few applications, an agent’s access footprint can span the entire enterprise in seconds.
- Indistinguishable requests. At the API level, there is no reliable way for an enterprise application to distinguish AI input from human input. When an agent calls an API, the request looks identical to one from a human user.
[AI Identity figure]
A biology analogy helps explain this. For a living organism to survive, it must sense its environment, identify threats, select responses, and execute them. This requires what researchers describe as an “I”: a model of oneself as a causal agent among other causal agents. A large language model (LLM) contains a sophisticated judgment engine, but a purely generative AI is not a causal agent. It gains that status only when it begins sensing and acting through protocols like Model Context Protocol (MCP), reading its environment, making decisions, and taking action.
The same expectation that applies to any human actor should also apply to an AI agent: if it is continuously sensing, judging, and acting, it should have its own unique identity and credentials bound to that identity.
▶️ Watch the Identity Problem Nobody Owns episode of A Walk in the Park.
Read this blog to dive deeper into what every security and AI leader needs to know.
The static credential problem: why API keys and passwords fall short
Traditional authentication mechanisms (such as API keys, Open Authorization (OAuth) client secrets, passwords, and static tokens) were designed for a different era. They fail in AI environments across multiple dimensions.
No reliable origin verification. Static credentials provide no way to establish the true origin of an action. A user who does not understand expected interaction patterns might paste an OAuth client secret into an AI chat, potentially exposing it as LLM training data. An agent could extract an API key from a configuration file it crawled. In both cases, there is no reliable way to ensure each action is authorized in a way the actor cannot deny. The fundamental security principle of non-repudiation, therefore, collapses.
Inspection and management failures. Static keys generally cannot be mapped to a specific subject by inspection. Legitimate, working keys cannot be distinguished from invalid or untrusted keys without additional context. The secret itself does not embed information about what policy it was issued under, and there are no uniform controls to enforce appropriate credential rotation.
No data protection. Client secrets do not provide encryption. Even if a static credential were suitable for identity verification, it would not protect data in transit.
Dangerous at AI scale. These shortcomings, manageable in limited human-centric deployments, become dangerous when amplified by AI agents operating at machine speed. A compromised agent can move laterally across systems without hesitation. A misconfigured agent can overstep boundaries in ways that look, from the outside, like deliberate abuse.
Currently, most organizations rely on API keys, symmetric keys, or static tokens. Only 54% use digital certificates for AI agent identity today, according to Keyfactor’s AI identity survey. This mix reflects a transition. Most organizations recognize the need for stronger identity but many still rely on mechanisms that were never designed for autonomous behavior.
Researchers worry most about over-trusted AI, not malicious AI. Many AI deployments quietly reintroduce the same anti-patterns the security industry has warned about for years – hard-coded credentials, shared secrets, and long-lived access – in the name of speed and experimentation.
Certificate-based identity: the foundation for AI trust
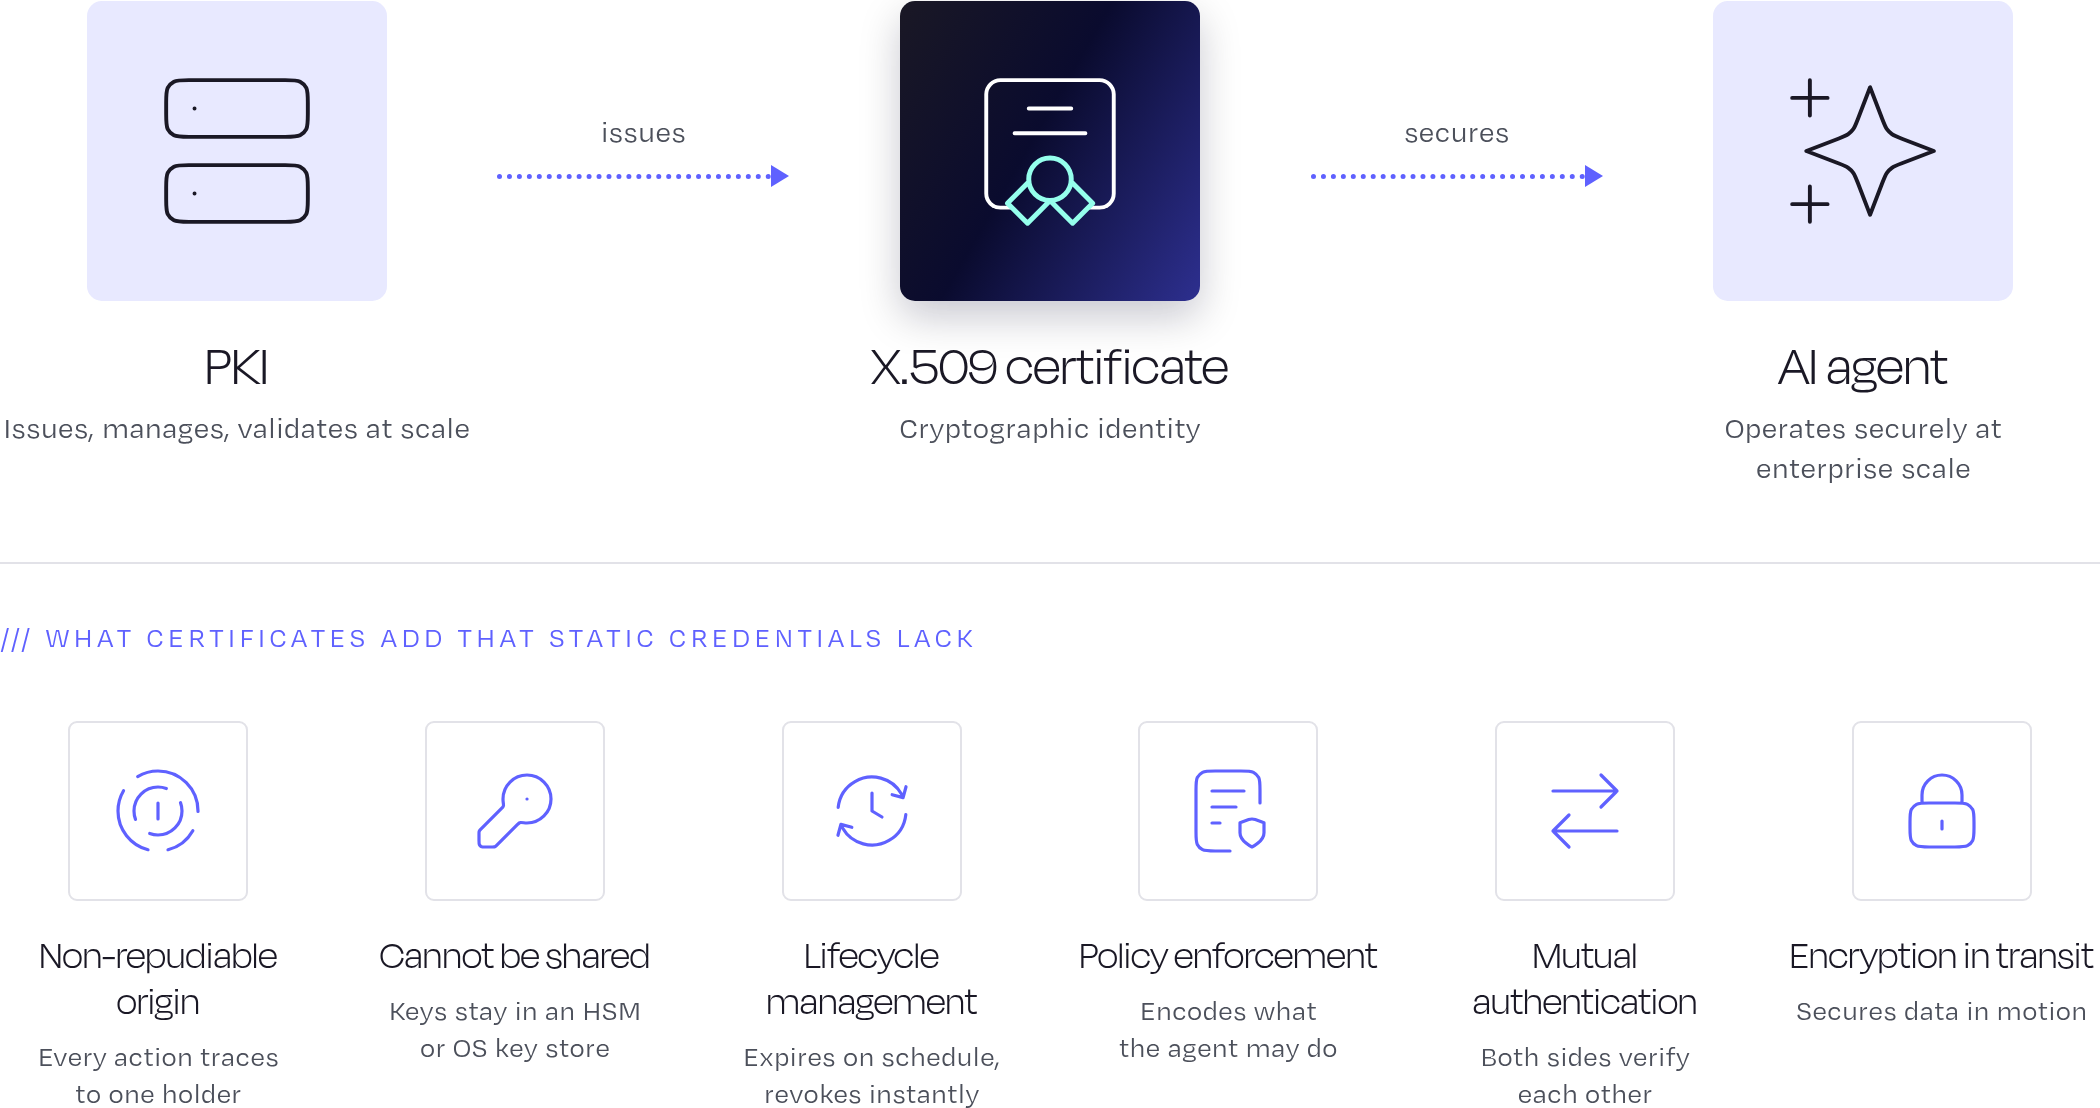
X.509 digital certificates solve the problems that static credentials cannot. They are the most widely deployed standard for digital certificates and provide the cryptographic foundation that AI agents require to operate securely at enterprise scale.
Certificates deliver six critical properties that static credentials lack:
- Non-repudiable origin. Every action can be traced back to a specific certificate holder. There is no ambiguity about which entity performed an action.
- Cannot be accidentally shared. Private keys can remain securely stored in a Hardware Security Module or operating-system-managed store, never appearing in chat logs or configuration files.
- Built-in lifecycle management. Certificates have defined lifespans and can be revoked immediately when compromised. Expiration is a feature, not a failure mode.
- Policy enforcement. Certificate extensions can encode specific authorization policies and constraints, such as which systems the agent can access, what operations it is authorized to perform, time-based restrictions, and compliance requirements. The certificate itself becomes a policy enforcement point.
- Mutual authentication. Both parties in a communication cryptographically verify each other’s identity, eliminating the possibility of impersonation.
- Encryption in transit. Certificates do not just identify endpoints, they also provide a secure channel for data transmission.
Public Key Infrastructure (PKI) is the system that issues, manages, and validates these certificates at scale. PKI provides the cryptographic foundation for establishing and maintaining secure identities across an organization’s entire agent ecosystem.
Modern implementations OAuth deployments are increasingly replacing static secrets with client certificates, resulting in a stronger client authentication. For interactive AI (where a human works alongside an AI agent through protocols like MCP) the user’s client certificate authenticates to the Identity Provider, which issues scoped OAuth access tokens. AI actions are performed under the user’s delegated authority with a full audit trail. For autonomous agents, the agent’s own workload certificate authenticates directly, and the Identity Provider (IdP) issues tokens based on the agent’s pre-configured authorization scope.
This approach eliminates the risks of static client secrets while preserving the scalability and flexibility of modern OAuth frameworks.
For containerized AI workloads, Secure Production Identity Framework for Everyone (SPIFFE) automates the entire certificate lifecycle. Each container receives a unique SPIFFE ID, and the runtime automatically issues short-lived X.509 certificates. Mutual TLS is established automatically between workloads, with zero operational overhead, even for ephemeral agents that exist for minutes.
[X509 certificates for ai agents figure]
Extending Zero Trust to AI: “never trust, always verify” for non-human actors
Zero Trust architecture operates on a foundational principle: never trust, always verify. Every communication link requires both parties to be authenticated and authorized, regardless of network address or previous access history. While Zero Trust has traditionally focused on human users and known applications, the rise of agentic AI demands that the model extend to autonomous systems.
In a Zero Trust environment secured by PKI, every entity, whether it is a human, an AI agent, a service, or a device, must present cryptographic proof of identity before accessing resources:
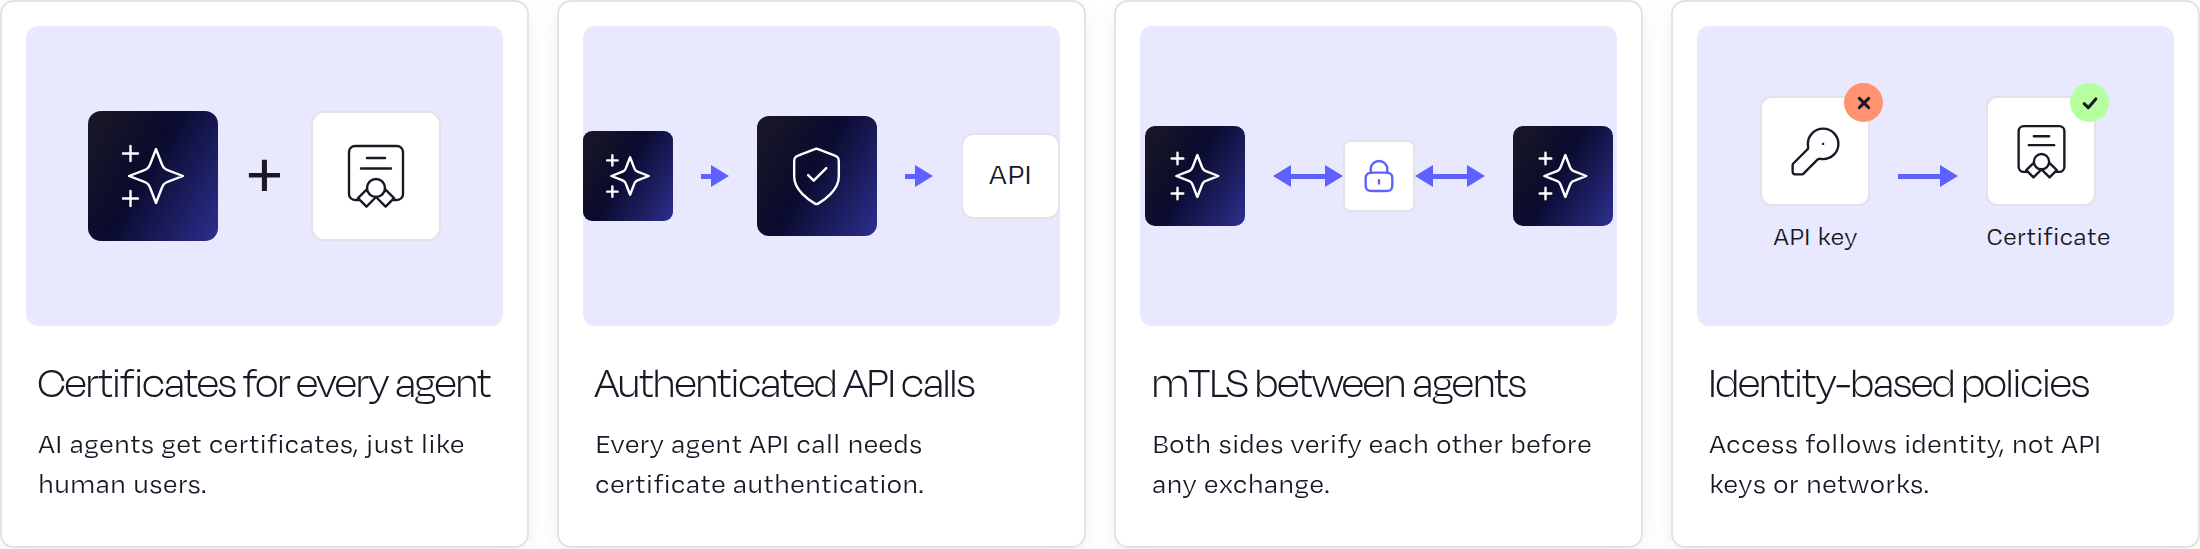
- AI agents need certificates just like human users need certificates.
- Every API call from an AI agent must have certificate authentication enforced.
- Agent-to-agent communication requires mutual TLS (mTLS) authentication.
- Resource access is governed by identity-based policies, not API keys or network-based controls.
With this foundation, Zero Trust shifts from a network security philosophy to an operational framework for autonomy. Every action an agent takes can be authenticated and authorized the moment it occurs. Every connection, whether agent-to-database or agent-to-agent, can be verified through mTLS. When an agent misbehaves or its behavior changes unexpectedly, its identity can be revoked instantly, isolating the risk without disrupting other workloads.
[Zero Trust figure]
Where traditional Zero Trust breaks down
Traditional Zero Trust assumes human-centric patterns, for example, predictable working hours, stable behavioral baselines, human-scale speed, device-based trust signals, etc. AI agents violate these assumptions in several ways:
Identity becomes behavioral, not just credential-based. A human has a stable identity through single sign-on (SSO), certificates, and multi-factor authentication (MFA). An AI agent running tool calls may share a credential across all invocations. Zero Trust for AI must layer behavioral identity on top. The agent’s action trajectory (i.e. the agent’s past) becomes part of its trust score.
Least privilege must be intent-scoped, not just role-scoped. For humans, organizations grant “read access to storage bucket X.” For AI agents, access must be scoped to task intent. That is, the agent should only call tools that are plausibly necessary for its declared task. This requires a policy layer that understands not only control lists to access resources, the context for each task.
Continuous re-evaluation mid-action. Humans perform discrete actions and log out. AI agents execute chains of tool calls where the risk profile changes mid-chain. Zero Trust for AI requires intra-session policy re-evaluation. After each tool call, the system must re-score whether the next requested action remains within trust bounds given what has already happened.
The prompt is an attack surface. There is no human analog to prompt injection. Zero Trust for AI must treat the input channel itself as untrusted. A retrieved document or external API response can carry adversarial instructions that attempt to escalate an agent’s privilege mid-task.
These adaptations represent a meaningful evolution of Zero Trust principles, but they do not overturn the core framework. They extend it to accommodate actors whose value lies in adaptability and autonomy.
Managing AI identity at scale: lifecycle, automation, and observability
The operational reality of managing identity for potentially thousands of short-lived AI agents forces PKI to evolve in three key ways.
Shorter lifetimes
AI agents rarely require long-term identity. Short-lived certificates (the ones valid for minutes or hours rather than months) reduce exposure and limit the blast radius when credentials are compromised. In most cases, there is no need for a certificate to outlive the agent it was issued to. Expiration becomes a security feature, automatically cleaning up credentials that are no longer needed.
Full automation
Manual certificate management becomes untenable almost immediately at AI scale. Issuance, renewal, rotation, and revocation must be automated end to end. Certificates must be issued automatically as part of agent deployment pipelines, orchestration platforms, or mesh admission workflows. Human involvement in routine identity operations simply does not scale.
Policy-driven identity
Authorization decisions must be encoded into identity policies and certificate templates rather than handled through exceptions and manual controls. Certificate templates can encode agent capabilities and constraints, ensuring that policy enforcement happens at the identity layer – not as an afterthought.
Service meshes as enforcement layers
Service meshes are emerging as a practical control point for workload identity, including AI agents. They sit at a natural enforcement layer in containerized deployments where they can distinguish one workload from another, observe which workloads are communicating, enforce mutual TLS by default, validate workload identity claims, and regulate which identities are allowed to interact.
In this context, certificate issuance becomes part of workload admission and orchestration rather than a standalone security process.
Agent classification
Not all AI agents are created equal. Organizations should classify their agents based on four dimensions:
- Access privileges: what systems and data they can touch
- Decision authority: what actions they can take without human approval
- Risk exposure: the potential impact if the agent is compromised
- Lifespan: whether they are persistent services or ephemeral workers
High-privilege, long-lived agents warrant stronger certificate policies and more frequent monitoring than limited-scope, short-term agents.
Identity-centric observability
Logs, telemetry, and alerts must be tied to cryptographic identity so that actions can be attributed accurately. If you cannot answer which agent performed an action, you do not have meaningful control. Identity-centric observability closes the gap between what happened and who did it.
AI identity governance and compliance
AI identity governance is emerging as one of the most consequential and underdeveloped areas of enterprise security.
The current state
In Keyfactor’s AI identity survey, only 50% of organizations report fully implemented governance frameworks for AI agents. The other half are still planning or in informal discussion. AI adoption is accelerating, but governance maturity is uneven.
The risk is not that organizations are unaware of the problem. It is that implementation lags behind operational reality.
In the same survey, 55% say their own leadership does not take the digital identity risks of agentic AI seriously enough. That gap shows AI risk is often recognized at the technical level before it is owned at the executive level.
Expectations around resilience remain low. Only 28% believe they could stop a rogue AI agent before damage occurs. Most expect detection or response only after an incident has begun.
The operational risks of autonomous authority
AI agents inherit permissions that were designed for convenience, not accountability. “Temporary” access has a long history of becoming permanent. With autonomous agents, those compromises become dangerous.
Least privilege in the age of agents is not a static policy. It is a real-time negotiation between capability and constraint. It requires dynamic privilege assignment, strong contextual awareness, and continuous validation of intent. It also forces a confrontation with a question that sits beneath the surface of every governance discussion: who is accountable when an autonomous agent misuses access?
Identity churn and continuous evidence
Short-lived agents create identity churn that traditional governance models were never designed to handle. Identities may exist for minutes or seconds, requiring continuous issuance and rotation, frequent revocation without service interruption, and high volumes of east-west traffic between agents.
Risk and compliance teams will increasingly require continuous evidence rather than point-in-time controls. Auditors are shifting their focus from model design to operational behavior: how an AI agent authenticates before acting, how its actions are logged and attributed, how quickly its access can be revoked, and whether decisions can be reconstructed after the fact.
The convergence ahead
AI governance today often lives in parallel with security and identity programs. Over the next several years, that separation will collapse. In Keyfactor’s survey, 85% agreed that digital identities for AI agents will become as common as human and machine identities within five years.
Identity will become the connective tissue between access control, security enforcement, risk management, and lifecycle oversight. By the end of the decade, AI governance will not be a standalone initiative. It will be embedded into enterprise identity and security architectures, because that is where enforceable control already exists.
Governance without enforceable identity controls is governance in name only. Frameworks such as NIST AI RMF, ISO/IEC 42001, and the EU AI Act all depend on the ability to trace, attribute, and audit AI actions. Each assumes organizations can identify which AI agent acted, and under what authority.
For regulators, uneven maturity is often a precursor to formal mandates. The window to build identity foundations before regulation hardens is already narrowing.
Emerging frontiers: MCP, vibe coding, and AI-assisted PKI
Three forward-looking dimensions of AI identity illustrate how rapidly the landscape is evolving.
Model Context Protocol (MCP): giving AI “eyes and hands”
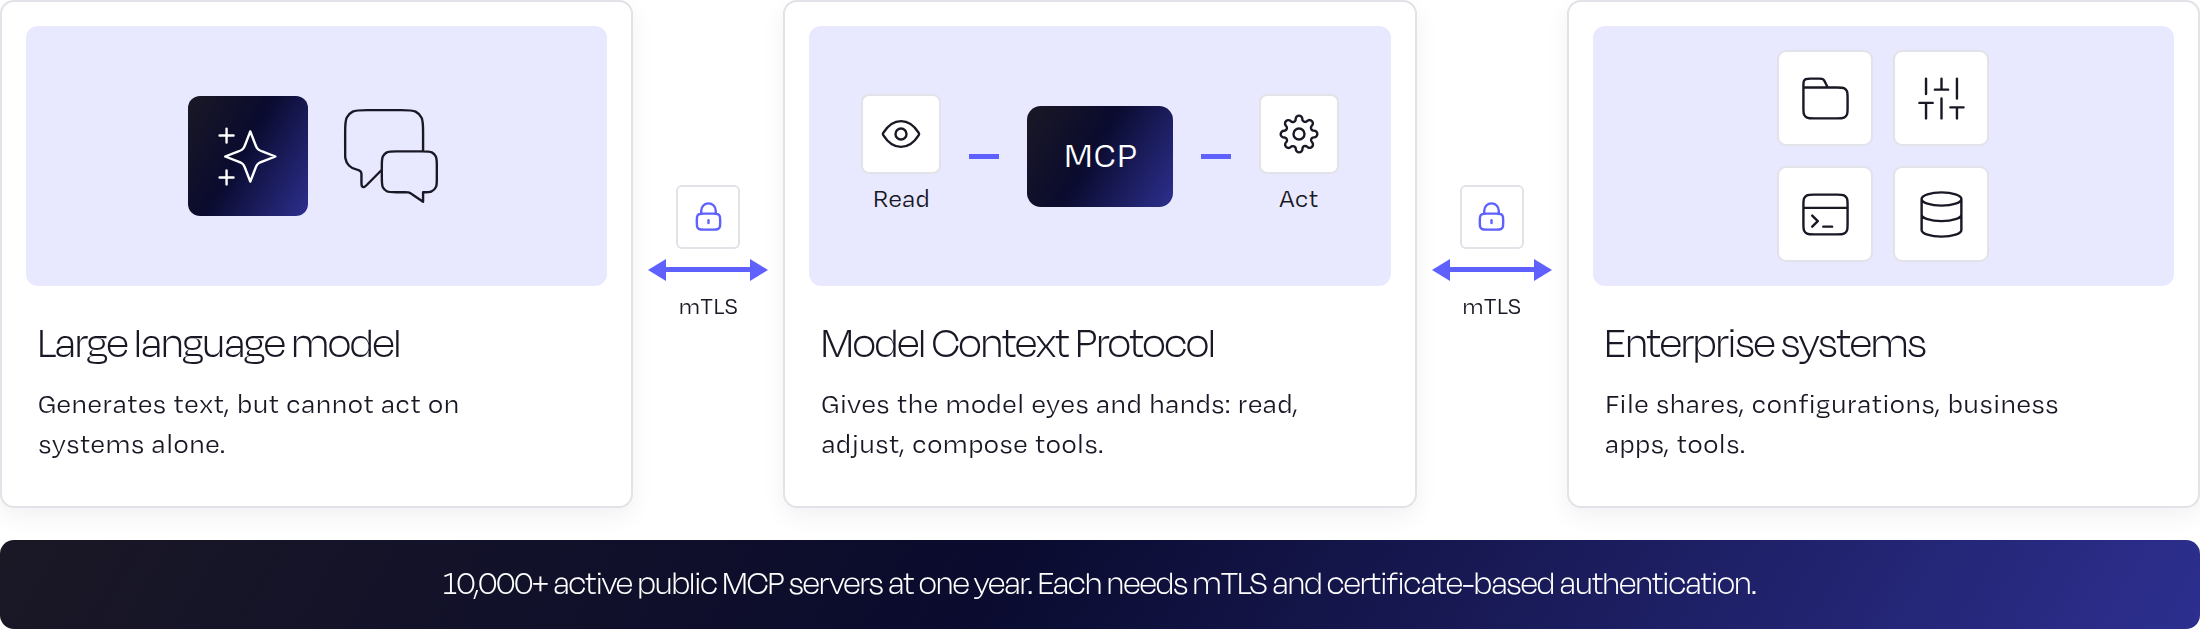
MCP is the protocol that transforms an LLM from a generative engine into an autonomous agent. MCP exposes enterprise systems to AI, letting agents read file shares, adjust configurations, interact with line-of-business applications, and compose multiple tools into workflows.
The scale is striking: at MCP’s one-year mark, there were more than 10,000 active public MCP servers, according to Anthropic, covering everything from developer tools to Fortune 500 deployments. As organizations scale agentic workloads, MCP is becoming a foundational layer, not a fringe technology, which is the HTTP of the AI era. And just like HTTP did before, it needs an identity and encryption layer to become enterprise-ready.
Securing MCP servers with mutual TLS and certificate-based authentication is critical. An MCP server exposes API functions to AI, and the AI can use its natural language capabilities to read the server’s documentation and use available operations dynamically, outside of any pre-programmed sequence. This means MCP servers must be locked down with proper certificate-based authentication, because the AI client is effectively a user of the application, generating traffic that the application cannot distinguish from the actions of a human.
[MCP Identity Figure]
Vibe coding and identity
In modern lingo, “vibe coding” is a term used to describe the process of writing code through natural-language prompts rather than keystrokes. Developers describe what they want, and an LLM drafts the logic. The productivity gains are real: prototypes appear in record time, and junior engineers can move at senior pace.
But vibe coding breaks the traditional chain of authorship and review. When a developer asks an LLM to “fix this bug” and the resulting patch introduces a vulnerability, who authored that logic? The developer? The model? The training data?
Just 32% of organizations report adequate visibility and governance over AI-assisted coding, according to Keyfactor’s survey. That is a growing blind spot in DevSecOps and software supply-chain risk.
Identity is the solution. Cryptographic provenance and code signing bring accountability to AI-generated code through several mechanisms:
- Cryptographically sign all code changes, either human or AI, ensuring every line has a verifiable author
- Require identity-backed authentication for commits so that AI agents interact with repositories under unique, cryptographically bound identities
- Validate and sign prompts before models generate code, creating defense against prompt injection
- Deploy secure pipelines with static analysis, dependency checks, software bill of materials (SBOM) creation, and vulnerability scanning at build time
As software development evolves toward a future where developers and AI agents co-author code, every AI contribution must carry a cryptographic fingerprint, every code path must have auditable provenance, and every commit must have an attributable identity.
AI as an operational lever for PKI
As AI agents proliferate, the complexity of managing cryptographic identity increases sharply. AI itself is becoming part of the solution.
Organizations are beginning to adopt AI-assisted PKI operations:
- Natural-language interfaces for certificate management – enabling administrators to manage certificates through conversational prompts rather than specialized tooling
- Autonomous discovery of cryptographic assets – AI agents that identify certificates, keys, and configurations across the enterprise
- Policy-driven issuance and renewal – automated certificate lifecycle management that responds to policy changes in real time
- Intelligent detection of misconfigurations and anomalies – AI-powered monitoring that identifies problems before they cause outages or security incidents
These capabilities are not about replacing PKI teams, they enable teams to operate at the tempo autonomous systems require.
How Keyfactor can help
Keyfactor brings these AI identity principles to life through a platform purpose-built for digital trust at enterprise scale. Trusted by the world’s largest enterprises to issue and manage billions of certificates across devices, workloads, and now AI agents, Keyfactor provides the cryptographic foundation for secure agentic AI deployment.
Core capabilities for AI identity
Unique X.509 certificates for every AI agent. Each agent receives a cryptographically-backed, non-replicable identity through Keyfactor’s EJBCA Enterprise PKI platform, a complete, flexible PKI with the scalability demanded by modern enterprises.
Certificate-based OAuth flows. Replace static client secrets with client certificate authentication for both interactive AI (human + AI via MCP) and fully autonomous agents. Every action becomes traceable to a specific certificate holder.
Mutual TLS for all AI communications. Enforce mTLS for agent-to-service and agent-to-agent communication, ensuring that every connection is cryptographically verified.
Automated certificate lifecycle management at AI scale. Keyfactor Command monitors and manages certificate lifecycles across any CA solution, providing bulk revocation and provisioning, real-time health monitoring, and the crypto-agility needed for evolving standards. SPIFFE integration enables zero-overhead certificate management for containerized AI workloads.
Policy-driven certificate templates. Encode agent capabilities and constraints directly into certificate templates – which systems agents can access, what operations they can perform, and time-based restrictions on activity.
MCP Server for Keyfactor Command. A natural-language interface for certificate management, enabling AI-assisted PKI operations that compress hours of administrative work into conversational prompts.
Risk intelligence and identity-centric observability. Monitor certificate usage, detect anomalies, score security posture, and receive real-time alerts for policy violations, all tied to cryptographic identity.
Crypto-agility and post-quantum readiness. As AI agents scale, so does the need for certificates. Keyfactor ensures organizations can issue, manage, and replace certificates at scale while staying agile and quantum-ready.
Secure code signing. Keyfactor SignServer provides an API-driven signing engine for fast, secure signing in virtually any format, including secure code signing and prompt signing. This is critical for maintaining provenance in vibe coding environments.
The deployment roadmap
The transformation to PKI-secured agentic AI follows a logical progression:
Phase one: Establish Zero Trust foundations. Before deploying a single AI agent, establish PKI-based Zero Trust for the systems agents will interact with. Assess the target environment, deploy certificate-based authentication, configure Identity Providers for certificate-backed OAuth, secure MCP servers with mTLS, and establish monitoring infrastructure.
Phase two: Deploy your first secure agent. Choose a low-risk, high-value use case. Provision the agent’s cryptographic identity. Test both interactive and autonomous authentication flows. Monitor certificate health and document repeatable patterns.
Phase three: Scale to billions with automation. Automate certificate enrollment in deployment pipelines. Deploy SPIFFE for containerized agents. Establish certificate templates for policy-driven identity. Expand the Zero Trust perimeter as use cases grow. Deploy AI-assisted certificate management and plan for post-quantum transitions.
Keyfactor gives security teams visibility and control over the identities and cryptography that secure every digital interaction, so your business keeps running—uninterrupted.

Frequently asked questions
Got AI Identity questions?
We’ve got answers.
Subscribe to The Source
Stay ahead of the curve with Keyfactor’s monthly newsletter — packed with curated insights, expert tips, must-watch videos, and practical guides to help you stay secure, agile, and quantum-ready.